How to Create Custom Code Review Rules for Codex with AGENTS.md: Complete Repository Governance Playbook
Introduction
This playbook is a practical guide for repository owners and platform teams who want to define, enforce, and evolve custom code review rules for Codex using AGENTS.md. It assumes teams run automated reviews with annotations such as @codex review and use the automatic review workflow that surfaces prioritized findings (P0/P1). The goal is not to describe every Codex API surface; instead, this document shows governance patterns that translate automated findings into repeatable rules, branch protection gates, reviewer assignment, and remediation workflows that scale across monorepos and modular codebases.
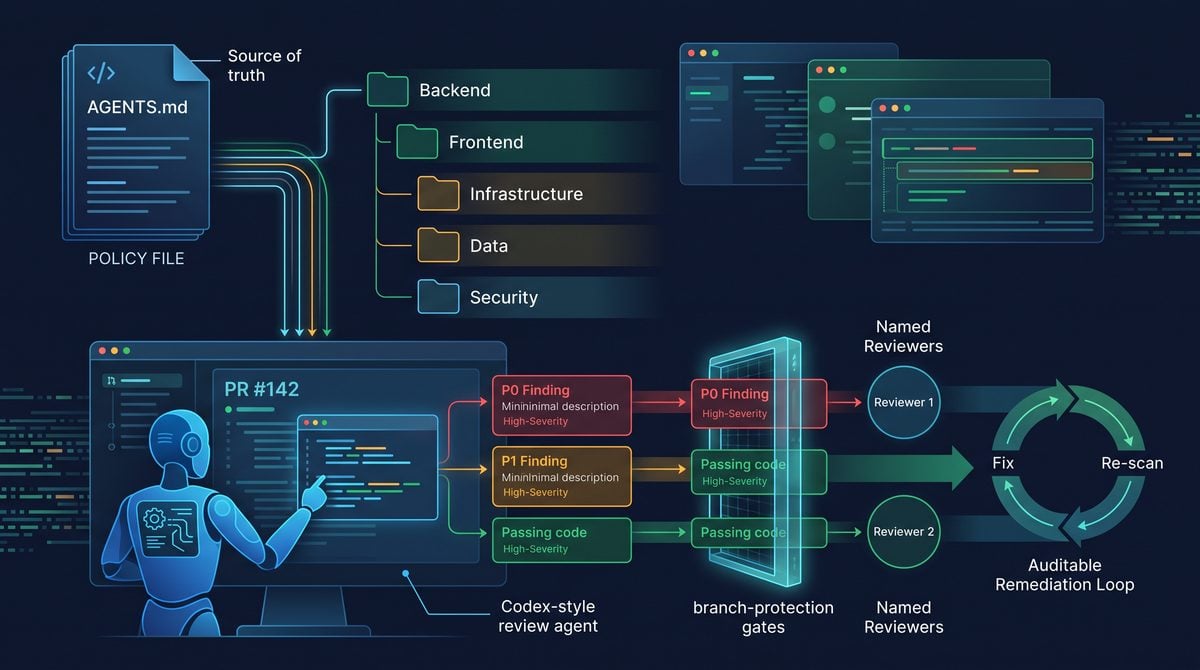
Successful repository governance treats code review rules as living policy: rules must be auditable, scoped to the right code areas, resilient to false positives, and able to escalate critical findings to an enforced, human-reviewed state. This first section frames the governance outcomes you should expect, summarizes the playbook structure, and explains how AGENTS.md files at the repository root and in nested directories inherit and specialize review rules. The inheritance model is foundational: it enables a single source of baseline policy while permitting directory-level teams to tighten rules where risk is highest.
Table of Contents for the Playbook
- Section 1: Introduction, governance outcome, and AGENTS.md inheritance model (this section)
- Section 2: Designing rule sets and severity mappings; branch protection and reviewer ownership
- Section 3: Reducing false positives and iterative rule tuning; monitoring and metrics
- Section 4: Auditability, change management, and remediation workflows including automated fixes
Within How to Create Custom Code Review Rules for Codex with AGENTS.md: Complete Repository Governance Playbook, the Rule Tuning and False Positives decision connects directly to The Codex Guardian Auto-Review Playbook — 10 Prompts for Automated Code Review, PR Feedback, and Quality Gates. That linked article specifically examines the Codex Guardian Auto-Review Playbook — 10 Prompts for Automated Code Review, PR Feedback, and Quality Gates, giving teams concrete background for applying the present article’s Rule Tuning and False Positives recommendations without duplicating this workflow’s scope.
Governance Outcome: What This Playbook Delivers
Adopting the patterns below should produce measurable governance outcomes that are visible across the development lifecycle. The outcomes focus on risk control, developer productivity, and organizational repeatability rather than on tool-specific implementation details.
- Consistent baseline enforcement: A repository root AGENTS.md establishes minimum mandatory checks and severity mappings so every change receives consistent baseline scrutiny regardless of which team owns a subdirectory.
- Scoped specialization: Nested AGENTS.md files allow teams to strengthen rules for sensitive areas (for example, authentication, cryptography, or infra provisioning) without creating global friction in lower-risk code paths.
- Clear reviewer ownership: Rules are mapped to owner teams or individuals so P0/P1 findings automatically route to the correct reviewers and avoid ambiguous escalation paths.
- Branch protection and gating: Critical findings (P0) become blocking conditions on protected branches while P1 findings raise high-priority issues that require timely remediation but do not necessarily block merges.
- Reduced noise and higher signal: Rule scopes, allowlists, and targeted exclusions reduce false positives; planned rule tuning prevents unattended noise growth.
- Auditable decisions and change history: Changes to AGENTS.md are reviewed like code, versioned on the default branch, and linked to review findings so auditors can trace why a rule was added or relaxed.
- Automated remediation with controlled guardrails: Use of automated helpers (for example an instruction such as @codex fix the P1 issue) is permitted for low-risk fixes, while human signoff is enforced for P0-level remediation.
How Root and Nested AGENTS.md Files Inherit and Specialize Rules
AGENTS.md functions as a declarative place to document and persist the repository’s review rules. The most common and practical deployment pattern is a repository-level (root) AGENTS.md that defines the baseline policy and nested AGENTS.md files in subdirectories that refine that baseline. The following paragraphs describe the recommended inheritance semantics, typical merging strategies, and governance guardrails to prevent accidental weakening of critical rules.
Inheritance semantics (conceptual)
Treat the root AGENTS.md as the canonical baseline. It should define mandatory checks, severity mappings (for example which classes of findings are P0 vs P1), and organization-wide constraints that cannot be relaxed by lower-level policies. Nested AGENTS.md files should be allowed to do three things:
- Declare additional rules that apply only to their directory tree.
- Tighten severity for specific rule classes within their scope (for example raising certain security checks from P1 to P0 for a crypto module).
- Introduce scoped allowlists or exceptions for generated code and third-party vendored directories, documented with rationale and a planned expiration where appropriate.
In practical terms, inheritance should behave like a union of rules with clear precedence: when a nested file defines a rule identical to a root-level rule, the nested definition takes precedence for files under that directory. When a nested file omits a rule, the root-level rule continues to apply. Governance must prevent nested files from silently disabling root-level P0 protections.
Precedence and merge model
| Precedence | Scope | Effect |
|---|---|---|
| 1 — File-level/nested AGENTS.md | Directory tree where AGENTS.md sits | Overrides or extends root rules for files in that tree |
| 2 — Root AGENTS.md | Entire repository default | Baseline rules applied unless overridden by nested files |
| 3 — Organization-level policy (if available) | Multiple repositories | Should set minimum constraints that repositories cannot lower |
Operationally, implement a deterministic merge: start from the root file, then walk up the directory path from the file to the repository root, applying nested overrides as you encounter AGENTS.md files. Avoid ambiguous merge strategies; explicit override semantics are easier to reason about during audit.
Practical patterns for specialization
Below are common patterns teams use to specialize rules in nested directories. Use them as templates rather than prescriptive schemas; the exact text structure of AGENTS.md may vary between environments.
- Hardening sensitive modules: A nested AGENTS.md raises severity for a misconfiguration or insecure API usage category from P1 to P0, ensuring branch protection blocks merges until a human review resolves the issue.
- Exempting generated code: A nested file explicitly marks a generated directory as exempt from stylistic or complexity checks while still surfacing security concerns. Exemptions must include a justification and a maintainer-signed approval.
- Per-package reviewer routing: Directory-level AGENTS.md maps rule categories to specific maintainer teams or individuals so critical P0 findings are routed to the right on-call or gatekeeper.
- Temporary experimental rules: Nested AGENTS.md can enable a trial rule for a limited scope with a stated sunset date and required monitoring, enabling incremental rollouts without repository-wide disruption.
Example (illustrative) AGENTS.md fragments
## Code Review Rules
# Root-level rules: baseline checks for the repository
- require-security-analysis: true
- severity-mapping:
    insecure-credentials -> P0
    weak-crypto -> P0
    missing-logging -> P1
- reviewers-on-p0: ["team-security"]

# Nested directory example: /auth-service/AGENTS.md
## Code Review Rules
# Augment root rules within /auth-service
- inherit: true
- tighten:
    weak-crypto -> P0
- allowlist:
    - path: vendor/
      reason: third-party vendored libs; periodic audit required
The snippet is conceptual: use a structured, human-readable “Code Review Rules” section in each AGENTS.md and keep rationale and owner information alongside each rule. Store AGENTS.md in the same repository so changes are tracked like code.
Governance guardrails to prevent policy weakening
Because nested AGENTS.md can relax rules, governance must enforce guardrails:
- Prohibit nested files from lowering the severity of root-level P0 rules; treat P0 as non-overridable by default.
- Require that any exception or allowlist entry includes a justification, expiration, and an owning person or team.
- Subject AGENTS.md changes to a review process that includes security and platform reviewers for policy-relevant edits.
- Maintain a changelog or commit message convention that references the governing ticket for auditability.
Operational checklist for initial rollout
Before deploying nested specialization broadly, complete this checklist to make adoption predictable and auditable:
- Publish a root AGENTS.md with baseline rules and owner contacts on the default branch.
- Map directories to owner teams using CODEOWNERS or an equivalent so reviewer routing is automatic.
- Document non-overridable rules (especially P0) and the process to request exceptions.
- Enable branch protection mappings that translate P0 findings into required status checks and required reviewers.
- Announce the rollout and run a pilot in a small set of directories to validate the inheritance behavior and false-positive rate.
Adopt a cadence for reviewing AGENTS.md files regularly: a periodic audit prevents drift between the documented policy and actual team practices.
Designing high-signal P0/P1 rules
P0 and P1 findings should represent the small fraction of changes that require immediate human attention. High-signal rules minimize noisy alerts so on-call engineers and reviewers can treat each finding as actionable: they contain deterministic evidence, point to the exact offending diff or file, identify an owner, and include a clear remediation path. Aim for rules that are narrow in scope, reproducible across runs, and easy to verify by a reviewer without additional investigation.
Practical rule design balances sensitivity and specificity: sensitivity ensures you catch critical regressions, specificity minimizes false positives. Design rules to report only when the change materially increases risk or violates explicit policy. For example, a P0 rule should not fire on a comment change; it should fire when a secret is actually added to a committed configuration file, when a runtime flag disables an authentication check, or when infrastructure code tightens network exposure for production services.
The “## Code Review Rules” section in AGENTS.md
Use the repository’s AGENTS.md to declare centralized, human-readable rules under a dedicated header titled “## Code Review Rules”. Each rule entry should include a stable rule identifier, severity level, a plain-language rationale, narrow file/path scope, the concrete condition that triggers the finding, required owner/team, recommended remediation steps, and an enforcement action (audit-only, required fix, CI-failure). Keep the content concise so reviewers and audit logs can display the text verbatim.
## Code Review Rules

- id: backend-secrets-in-committed-config
  severity: P0
  title: "Committed secret in configuration file"
  rationale: "Committed secrets in repository configurations lead to credential leakage if not rotated."
  scope:
    paths:
      - "services/*/config/**"
      - "infra/**/secrets.yml"
  condition:
    - file_contains_regex: "(?i)access_key|secret|private_key"
    - diff_adds: true
  owners:
    - team: platform-security
  enforcement: require-fix
  remediation: "Remove the secret from code, move it to a secrets manager, rotate keys, and reference the secret by identifier."
That example shows the minimum fields that drive downstream automation and human workflows. The AGENTS.md format should be consistent across root and nested files so the agent can merge rules predictably.
Rule examples and patterns by domain
Below are illustrative patterns for backend, frontend, data, infrastructure, and security rules. Treat these as templates for specifying deterministic evidence and scoped matches rather than as prescriptive syntax for any tooling API.
-
Backend (P0 / P1)
- Rule: Disabling authentication checks in a request handler. Evidence: diff removes or bypasses authentication middleware, or conditionally returns user context without authentication. Owner: backend-service owners. Enforcement: P0, require-fix.
- Rule: Database credential hard-coded in source. Evidence: new file additions or modifications matching credential patterns inside application code. Owner: database-owners. Enforcement: P0/P1 depending on environment.
-
Frontend
- Rule: Insecure inclusion of third-party scripts on production pages. Evidence: changes to HTML/templates adding external <script> tags for production hostnames. Owner: frontend-security. Enforcement: P1, require review and risk assessment.
- Rule: Removing client-side input sanitization before sending to backend. Evidence: deletion of sanitization call sites in a diff with matching form handlers. Owner: frontend-team. Enforcement: P1.
-
Data
- Rule: Adding access permissions that widen data exports (e.g., granting read to public). Evidence: change to data-export scripts, ACL files, or access-control config. Owner: data-platform. Enforcement: P0 for production datasets, P1 for staging.
- Rule: Introducing a new ETL pipeline that writes raw PII to a non-compliant storage location. Evidence: new pipeline config referencing non-compliant buckets. Owner: data-compliance. Enforcement: P0.
-
Infrastructure
- Rule: Opening firewall ports to 0.0.0.0/0 for production services. Evidence: Terraform/CloudFormation/manifest diffs that set wide CIDR blocks on production resources. Owner: cloud-ops. Enforcement: P0, require-fix.
- Rule: Changing autoscaling policy to reduce redundancy below target thresholds. Evidence: a diff that lowers desired/replica counts beneath documented minimums. Owner: SRE. Enforcement: P1, require review.
-
Security
- Rule: Adding a dependency with an unresolved high-severity vulnerability. Evidence: dependency manifest changes introducing a package known to be high-risk. Owner: dependency-security. Enforcement: P0 for production-bound services.
- Rule: Disabling TLS validation in an HTTP client. Evidence: code changes that set insecure-flag or skip hostname verification in production branch. Owner: security-team. Enforcement: P0.
Repository layout examples and nested rules
Design your AGENTS.md layout so root-level rules capture global policies and nested AGENTS.md files specialize or tighten rules for subtrees. Use narrow scoping in nested files to reduce false positives and to reflect ownership boundaries. The following table gives a compact layout example and the intended rule inheritance behavior.
| Path | Primary Owner | Typical Rules | Inheritance Behavior |
|---|---|---|---|
| /AGENTS.md | org-security | Global security policies, secret scanning basics, infra network defaults | Base rules apply to entire repo unless overridden |
| /services/payments/AGENTS.md | payments-team | Payment-specific secret checks, PCI-scope data rules, network egress restrictions | Overrides or tightens root rules for /services/payments/** |
| /infra/production/AGENTS.md | cloud-ops | Strict port exposure rules, production region constraints | Stricter than root for infra production manifests |
In practice, the agent that evaluates rules should merge rule sets deterministically: nested files take precedence for matching paths, and unspecified fields fall back to root values. Document precedence clearly in the repo so contributors understand which rule will fire for their change.
False-positive reduction and iterative rule tuning
Start every new rule in an observation or “audit” mode for a minimum period. Run the rule against historical pull requests and commits to collect a corpus of true positives and false positives. Use that dataset to refine the rule scope, adjust regexes from greedy to anchored forms, add path-based exclusions, and introduce allow-lists for known safe patterns. Track the false-positive rate quantitatively before enabling enforcement.
- Run rules in shadow mode against main and long-lived branches; store findings in an artifact store.
- Sample findings and label them true/false with owner teams; calculate precision. Tune scopes and conditions until precision meets the team target for P0/P1.
- Add explicit negative matches and path exclusions directly in AGENTS.md rather than broadening the rule logic in ways that reduce sensitivity.
- Deploy rule with graduated enforcement: advisory → required-fix in CI → mandatory before merge for P0.
Within How to Create Custom Code Review Rules for Codex with AGENTS.md: Complete Repository Governance Playbook, the False Positive Reduction decision connects directly to How to Use OpenAI Codex for Automated Code Review: Setting Up PR Analysis, Security Scanning, and Performance Optimization Agents. That linked article specifically examines use OpenAI Codex for Automated Code Review: Setting Up PR Analysis, Security Scanning, and Performance Optimization Agents, giving teams concrete background for applying the present article’s False Positive Reduction recommendations without duplicating this workflow’s scope.
Reviewer ownership, branch protection, and enforcement
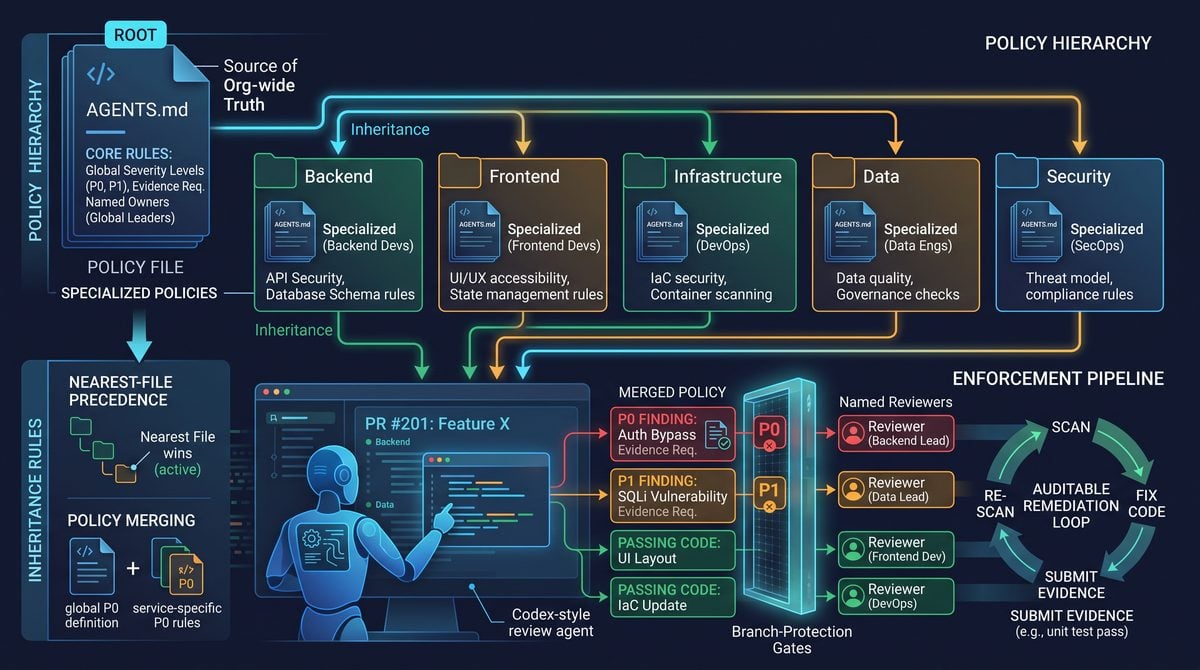
Pair code-review rules with explicit reviewer ownership and branch protection to ensure findings are resolved by the right teams. Maintain CODEOWNERS files aligned with AGENTS.md owners for path-level ownership. Configure branch protection rules that map severity to enforcement action: for example, require passing security checks and an approval from the owning team for P1 changes, and block merges until a required-fix P0 is resolved.
- Use CODEOWNERS to ensure at least one knowledgeable reviewer is auto-assigned for diffs that match rule scope.
- For CI enforcement, expose the agent results as structured status checks. Configure protected branches to require successful status for P0 or an explicit approval that includes a remediation plan.
- Allow an emergency escape hatch only when accompanied by an audited and documented exception that requires post-merge remediation within a short SLA.
Auditability and findings metadata
Every finding should produce a stable, machine-readable record that includes rule id, severity, exact diff hunk(s), file path, commit or PR identifier, timestamp, and the evaluated AGENTS.md version hash. Store these records as artifacts of CI runs and surface them in the code-review UI and any incident or change logs so reviewers and auditors can trace when and how a rule fired.
Retention policies for findings should align with incident response and compliance needs. Keep raw evidence long enough to support post-incident forensics and retrospective tuning. Ensure findings are linkable to tickets or remediation PRs for lifecycle tracking and reporting.
Remediation workflows
Design remediation steps for each rule to be short, prescriptive, and mechanizable. A remediation workflow typically includes automated suggestions (diff patches, configuration templates), an owner assignment, and an SLA. Where safe and deterministic, the agent can create an automated remediation PR that resolves a P1 and requests an owner’s approval; for P0s require a human-driven fix and an immediate revert or rollback plan if necessary.
Implement a triage path: the agent raises an initial finding, assigns it to the owner team, and either auto-creates a fix PR or annotates the original PR with a remediation checklist. Track remediation progress with labels and link the finding to an issue if the fix is non-trivial. For recurring or systemic findings, treat the remediation as a follow-up engineering project and track it separately from the immediate fix so root-cause work is prioritized.
Within How to Create Custom Code Review Rules for Codex with AGENTS.md: Complete Repository Governance Playbook, the Remediation Playbooks decision connects directly to Codex Security Masterclass: 30 Production-Ready Prompts for Automated Vulnerability Scanning, Patch Generation, and Security Code Review. That linked article specifically examines codex Security Masterclass: 30 Production-Ready Prompts for Automated Vulnerability Scanning, Patch Generation, and Security Code Review, giving teams concrete background for applying the present article’s Remediation Playbooks recommendations without duplicating this workflow’s scope.
Designing high-signal P0/P1 rules, placing them under a clear “## Code Review Rules” section, and pairing them with ownership, branch protection, and audit trails ensures that reviews scale without overwhelming teams. Use nested AGENTS.md to reflect ownership, iterate rules in shadow mode to reduce false positives, and automate safe remediation paths to shorten time-to-fix.
Section 3 — Review Execution, Triage, and Enforcement
Within How to Create Custom Code Review Rules for Codex with AGENTS.md: Complete Repository Governance Playbook, the Designing high-signal P0/P1 rules decision connects directly to Codex Background Tasks Masterclass: 30 Production-Ready Prompts for Autonomous Code Review, Refactoring, and Continuous Improvement. That linked article specifically examines codex Background Tasks Masterclass: 30 Production-Ready Prompts for Autonomous Code Review, Refactoring, and Continuous Improvement, giving teams concrete background for applying the present article’s Designing high-signal P0/P1 rules recommendations without duplicating this workflow’s scope.
Manual @codex review vs. Automatic review: when and how to use each
Two review modalities should coexist: automated, continuous analysis that runs on every push or pull request, and targeted, manual @codex review runs that are invoked by human reviewers for high-risk code or complex changes. Use automated reviews for broad coverage and initial gatekeeping; use manual reviews for focused, context-heavy investigations that require richer evidence collection or step-through reasoning.
- Automatic reviews (recommended default): Configure Codex as a CI job that runs on push and pull_request events and publishes a status check. Set the check to report P0/P1 findings as GitHub Check Run annotations and to post a summarized review comment on the PR. Keep automatic rules scoped to high signal checks (P0/P1) and non-invasive findings so the noise level remains low. Use nested AGENTS.md files to narrow rules to specific directories when different teams maintain different services.
- Manual @codex review: Allow reviewers to invoke @codex review comments in PRs when human context is required: complex security-sensitive logic, ambiguous spec changes, or crash-causing patches. A manual review should be able to run with a one-off focus (single file or function) and escalate with explicit reviewer instructions embedded in the comment body. Require reviewers to include the precise patch range or file paths to limit the review surface when desired.
One-off focus runs and targeted reviews
One-off focused reviews are essential for triage and quick cycles. There are two practical patterns to support focused invocations safely:
- PR comment scoping: Users comment with an explicit scope in the PR, for example a line-range, file path, or a single commit SHA. The bot then runs only on that scope and posts findings with inline annotations. Encourage a convention in your repository’s contributing doc that describes the allowed scope syntax.
- Ad-hoc CI job: Provide a workflow that accepts input parameters (file path, commit range) and runs the Codex review engine locally or in CI. This job can be used interactively by reviewers to create a deterministic, reproducible review artifact stored in the repo’s review archive.
Both patterns should record the AGENTS.md version used, the exact inputs, and a commit SHA for auditability (see the Auditability section below).
Security Review: specialized flow and evidence expectations
Security Reviews require faster triage, higher evidentiary standards, and an explicit remediation path. Treat Security Reviews as a superset of regular reviews with distinct handling rules:
- Rule set: Maintain a dedicated subsection in AGENTS.md for Security Review rules. Keep P0 definitions strict and conservative (e.g., exploitable credential leaks, command injection primitives) while P1 covers risky patterns requiring mitigation or manual verification.
- Evidentiary requirements: For any P0 or P1 security finding, require at minimum: the exact file path and line numbers, the commit SHA where the issue was introduced (or a short blame range), a minimal reproducible snippet or input that demonstrates the issue when applicable, an explanation tying the pattern to potential impact (e.g., remote code execution, sensitive data exfiltration), and a suggested remediation or hardening approach. The review artifact should also indicate whether the finding is exploitable in the current deployment configuration.
- Triage and ownership: Route Security P0s to the security on-call (SRE or dedicated security engineer) and create a tracking issue automatically. P0 findings should block merge until explicitly acknowledged and assigned; P1 findings may be allowed to proceed with an assigned remediation plan and scheduled fix window.
False-positive reduction and rule tuning
False positives are the primary friction point when adopting automated AI reviews. Reduce noise through progressive tuning rather than trying to eliminate all false positives upfront.
- Start with conservative priorities: Configure rules to surface only high-confidence P0/P1 results in the blocking check. Lower confidence or informational results can be posted in a non-blocking check or as a periodic report.
- Allowlist and ignore contexts: Use nested AGENTS.md to record directory-specific exceptions, allowlists for third-party generated code, and test fixtures that trigger patterns but are safe. Prefer explicit allowlist entries that cite the reason and an owner, rather than blanket file globs.
- Rule parameterization: Tune rules with threshold parameters where supported: complexity thresholds, data-sensitivity heuristics, or known safe APIs. Where a rule relies on pattern matching, prefer structural checks (AST or type-aware) to regex matching; structure-based checks are far less prone to accidental matches.
- Feedback loop: Implement a documented “invalid finding” pathway where reviewers can mark a finding as false positive. Each false-positive should be triaged, and if widespread, the originating rule should be updated with a more discriminating condition and a changelog entry in AGENTS.md.
Evidence requirements and review artifact model
Every actionable review finding should be accompanied by a compact, machine-parseable artifact that supports human triage and downstream automation. Define a review artifact schema and store artifacts as either attachments on the GitHub Check Run or in a repository directory dedicated to reviews.
| Field | Purpose | Recommended Content |
|---|---|---|
| finding_id | Unique identifier for cross-referencing | Stable string that includes rule_id and occurrence number |
| rule_id | Which rule produced the finding | Pointer to the rule’s section in AGENTS.md |
| severity | P0/P1/P2 classification | P0 or P1 for blocking or urgent follow-up |
| file_path / line_range | Where the issue resides | Path plus exact line numbers or code token ranges |
| commit_sha | Which commit introduced or contains the issue | Full or abbreviated commit SHA |
| evidence_snippet | Minimal reproducible example or code excerpt | 3–10 line snippet and a short rationale |
| confidence | Model confidence or heuristic score | Score with calibration guidance |
| recommended_fix | Suggested remediation steps | Patch summary, remediation rationale, or instruction to run @codex fix |
Store the artifact as a JSON or YAML file and link it in the PR comments and in the Check Run. Keep a retention policy for artifacts aligned with your compliance needs and log every review action (who ran it, when, AGENTS.md version).
Access 40,000+ AI Prompts for ChatGPT, Claude & Codex — Free!
Subscribe to get instant access to our complete Notion Prompt Library — the largest curated collection of prompts for ChatGPT, Claude, OpenAI Codex, and other leading AI models. Optimized for real-world workflows across coding, research, content creation, and business.
Branch protection and enforcement strategy
Branch protection is the enforcement layer that converts review findings into organizational policy. Integrate Codex results with branch protection in three dimensions: status checks, required approvals, and automated remediation gating.
- Status checks: Expose the Codex review as one or more status checks: a blocking check that only fails on P0 findings, and a non-blocking advisory check that reports P1/P2. This reduces accidental workflow interruption while ensuring critical issues block merges.
- Required approvers and ownership: Combine CODEOWNERS with review findings: if a P1/P0 arises in an area with a code owner, require that code owner to approve the PR after remediation. For security-critical directories, require a security approver or SRE sign-off before merge.
- Merge gating and remediation: For P0 findings, configure the protection rule to prevent merges until either the finding is fixed or an override process is followed (for example, a documented emergency waiver with audit trail). For P1 findings, allow merges only when a remediation ticket is linked and a deadline is set.
Remediation workflows and automation
Automate as much of the remediation lifecycle as policy allows, but require human verification for safety-critical fixes. Typical remediation patterns include:
- Auto-created issue with template: When a P1 or P0 is detected, automatically open a triage issue populated with the review artifact, severity, suggested fix, and default assignee (from CODEOWNERS or a security on-call rotation).
- Patch suggestion and @codex fix: Where the rule has high-confidence remediation, the system can generate a suggested patch and either open a draft branch or propose a fix PR. For P1 fixes this can be automated end-to-end; for P0 fixes require explicit human checkout and approval before merging. Use an explicit bot command such as @codex fix the P1 issue to request the automated patch and require a named reviewer to approve.
- Escalation path: Define escalation rules for overdue P1 issues and immediate alerts for P0. Integrate with on-call paging and ticketing to ensure visibility.
Best practice: never allow an automated fix for a P0 security finding to merge without a named security reviewer explicitly approving the remediation branch. This preserves both safety and an auditable decision trail.
Reviewer ownership, rotation, and audit trails
Clear reviewer ownership reduces triage time and distributes responsibility. Implement these operational controls:
- Assign by area: Use CODEOWNERS and AGENTS.md directory scoping so reviews and findings route to the team that owns the code. Where a finding spans multiple owners, create a composite assignment policy that designates a primary owner.
- Rotation and on-call: Maintain an on-call rotation for security and platform review duties. Include the on-call roster in AGENTS.md so the bot can assign or page the correct person.
- Audit logs: Record every review invocation, the AGENTS.md commit hash, the findings artifact, who triaged, and who approved remediation. Persist these logs in a team-accessible store and retain them per compliance requirements.
Nested directory rules: avoiding conflicts and predictable inheritance
When nested AGENTS.md files override root rules, follow these practices to avoid conflicting diagnostics and ensure predictable behavior:
- Explicit precedence: Define an explicit merge and override order in AGENTS.md documentation: child directory rules should annotate whether they append to or replace parent rules. Enforce the rule that replacement only occurs when the child file explicitly declares intent.
- Local minimums: Use local rules to tighten, not loosen, critical security requirements. If a directory needs an exception, prefer allowlist entries rather than removing a parent security rule entirely.
- Conflict detection: Add a pre-commit or CI check that validates AGENTS.md merges and flags contradictory rule changes so owners can resolve them before a review run.
Operational checklist for enabling Codex reviews on a repository
- Define the blocking policy: decide which findings are P0 and must block merges.
- Implement CI workflows: add automatic Codex checks as separate status checks for blocking and advisory findings.
- Configure branch protection: require the blocking Codex check and the appropriate approvers for sensitive directories.
- Document manual review commands and focused-scope syntax in CONTRIBUTING.md so reviewers know how to run targeted @codex review sessions.
- Establish an incident and escalation policy for P0 findings that includes on-call paging and mandatory audit log entries.
- Create a feedback loop for false positives and a process for updating AGENTS.md with clear change notes and owners.
Remediation workflows: automated fixes, ownership, and escalation
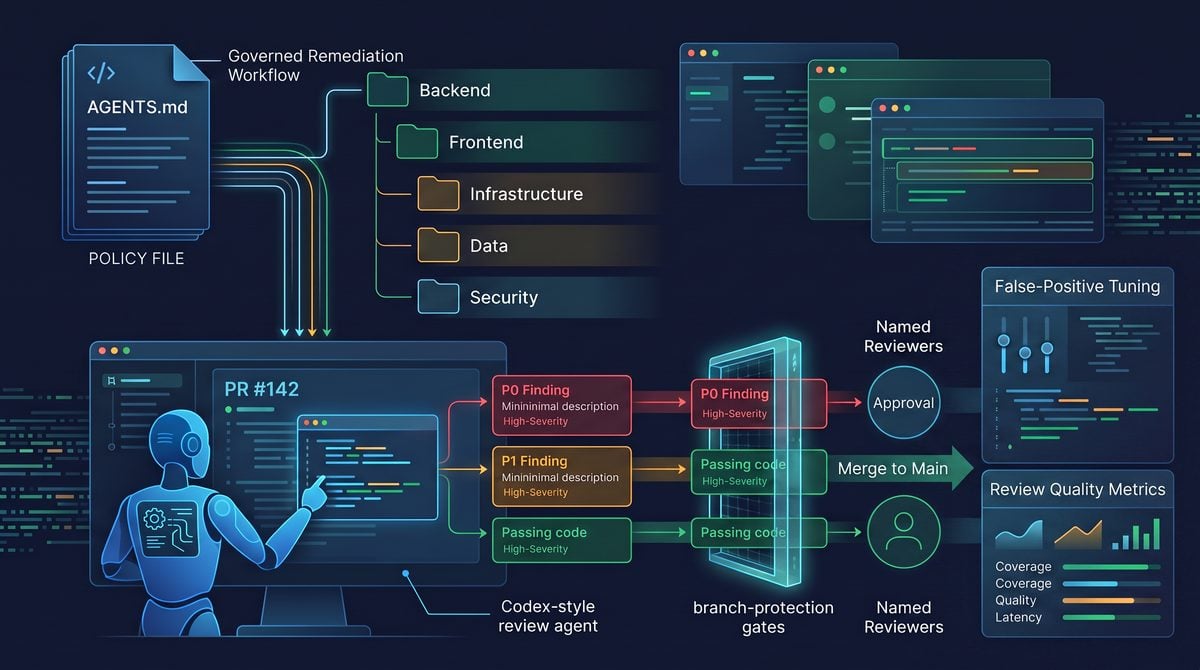
Remediation is where repository governance delivers value: clear findings must translate into traceable, tested changes. This section prescribes practical workflows that combine Codex reviews, automated remediation via the @codex fix the P1 issue pattern, human approval gates, ownership and escalation rules, and measurable telemetry so teams can iterate on rules without disrupting delivery.
The patterns here assume your repository already exposes high-signal P0/P1 rules in AGENTS.md and that you have branch protection and reviewer ownership configured. The objective is to treat Codex findings as first-class artifacts—discoverable, reproducible, auditable, and reversible—while minimizing noise and friction for contributors.
@codex fix the P1 issue: safe automated remediation
Use automated fixes for straightforward, low-risk P1s (for example, a missing import, a small security header configuration, or an agreed lint rule). The automation pattern should follow these rules of engagement:
- Conservative scope: automatic patches should be limited to single-file, mechanical edits or configuration changes with deterministic outcomes.
- Generate a patch branch: the bot should create a descriptive branch and a pull request (PR) from the patch branch to the originating branch rather than committing directly to protected branches.
- Run CI and tests: the generated PR must run the full pipeline required by branch protection. Automatically merge only after passing CI and receiving required human approvals; do not auto-merge simply because the bot authored the PR.
- Attach review evidence: the PR body must include the finding ID, relevant lines of code, a short remediation rationale, links back to the triggering Codex review, and an artifact of the original diff for auditability.
- Allow fast rejection: humans must be able to revert or close the auto-fix PR quickly. Ensure the PR is clearly labeled and documented so reviewers can decide without hunting context.
Example PR body template (illustrative):
Title: codex/fix/P1-<finding-id> - fix missing security header

Body:
- Trigger: Codex review ID <id>, P1: missing Strict-Transport-Security header
- Change: add header to configuration in file/path/config
- Tests: existing unit and integration tests ran in CI; no test changes required
- Rationale: mechanical fix aligned to org policy XYZ
- Audit: original Codex review attached at /.codex/reviews/<id>.json
Constrain the @codex fix capability by permission: the automation bot should only create branches and PRs. The ability to merge should remain with the code owners or designated maintainers until confidence in fixes reaches an organizational threshold.
Ownership, SLAs, and escalation paths
Define clear ownership for each rule and for remediation workflows. Ownership minimizes queueing and ensures someone is accountable when the bot cannot confidently remediate an issue.
- Rule owners: every rule in AGENTS.md should include an owner attribute (team or individual) and an on-call rotation if the owner is a team. If a rule has no owner, treat findings as advisory until an owner is assigned.
- SLA tiers: codify response and remediation SLAs by priority. A typical structure is a short response SLA for P1 triage (for example, acknowledge and either remediate or schedule within the same workday) and a longer remediation SLA for completing human-reviewed fixes.
- Escalation channels: establish an escalation path (team chat channel + escalation contact) and integrate automated alerts into that channel for high-severity findings that are not auto-fixed within the SLA.
- Ownership metadata: record ownership details in AGENTS.md rule metadata and surface them in PRs and review artifacts so reviewers know whom to ping.
Maintain a lightweight runbook per owner describing how to triage a failing rule, how to evaluate a proposed auto-fix, and when to mark a finding as false positive. This runbook should be discoverable from the Codex review output.
Metrics, telemetry, and dashboards
Measure the governance system itself. Track metrics that highlight signal quality, remediation effectiveness, and operational health. Collect telemetry from review runs, automated fixes, and human actions; store artifacts centrally to support audits and post-incident analysis.
| Metric | What it measures | Use |
|---|---|---|
| P0/P1 count (per week) | Number and trend of high-priority findings | Detect rule regressions or new hotspots |
| MTTD (Mean Time to Detect) | Time between code submission and first Codex finding | Assess review cadence and rule coverage |
| MTTR (Mean Time to Remediate) | Time from finding creation to resolved state (merged fix or accepted exception) | Evaluate remediation workflow effectiveness |
| False-positive rate | Share of findings marked as false positive by owners | Guide rule tuning and reduce reviewer noise |
| Auto-fix acceptance rate | Share of @codex-created PRs merged vs closed | Measure trust in automated remediation |
Implement lightweight instrumentation: collect timestamps for review creation, patch PR creation, CI events, approvals, and merge events. Store review JSON artifacts and CI logs alongside the issue/tracking ticket or in a centralized object store. Dashboards should be updated daily and alert when MTTR for P1s exceeds policy thresholds.
Phased rollout: canary, shadow, advisory, and enforcement
Roll rules and automated fixes in controlled phases to reduce disruptions and build confidence:
- Shadow mode: run rules on PRs and store findings without posting comments or opening issues. Use this to measure signal and false-positive rates on real diffs.
- Advisory mode: post findings as PR comments or statuses but do not block merges. This phase tunes messaging and evidence requirements so reviewers understand the finding context.
- Canary enforcement: enforce a subset of repositories or a percentage of branches. In this stage enable @codex fix for low-risk findings only and require human approval for merges.
- Full enforcement: enable branch protection gates for P1 findings across all repositories. Only enable auto-merging of bot PRs after the auto-fix acceptance rate and test pass rate reach target thresholds.
For each phase, define quantitative exit criteria: acceptable false-positive rate, MTTR target, and auto-fix acceptance rate. Iterate quickly between phases based on measured metrics and owner feedback.
Complete remediation checklist
Use this checklist when enabling a new rule or rolling a change to remediation behavior. Teams can use it as a gate before increasing enforcement severity.
- Run a shadow period of representative repositories and collect at least one full release cycle of data.
- Validate evidence outputs: ensure review artifacts include snippet, file path, and rule rationale.
- Confirm owner assignment in AGENTS.md and that runbooks exist for each owner.
- Verify the auto-fix produces an isolated patch branch and descriptive PR with CI enabled.
- Set up alerts for SLAs and dashboards for the metrics table above.
- Conduct a triage tabletop where owners review representative auto-fix PRs and simulated escalations.
- Gradually increase enforcement scope (canary → full). Re-check metrics at each step against exit criteria.
- Document exception processes and how to record accepted risk in the issue tracker for auditability.
Troubleshooting common remediation failures
Many failures are operational rather than conceptual. Below are common failure modes and recommended remedies.
Auto-fix PRs fail CI
Symptoms: auto-fix PRs fail lint or unit tests. Remedies: ensure the bot runs the same pre-merge pipeline as human contributors; if tests are flaky, quarantine the rule and tune the fix to be less invasive or add missing test changes to the generated PR. If CI failures are environmental, surface CI logs in the PR and assign to CI/system owners.
Conflicting fixes from multiple rules
Symptoms: two different rules propose overlapping edits or one nested rule overrides a root rule fix. Remedies: define a deterministic precedence model in AGENTS.md rule metadata and have the remediation engine merge fixes according to priority. If conflicts persist, generate a combined human-review PR with both suggested edits and an explanation of the conflict.
High false-positive rate after rollout
Symptoms: owners or contributors frequently close auto-fix PRs as irrelevant. Remedies: revert the rule to advisory, run a wider shadow period, collect representative contexts, and refine the rule’s matches (narrow patterns, add required evidence, or increase the minimum confidence threshold). Record false-positive examples to guide rule tuning.
Bot lacks permissions or creates too many branches
Symptoms: permission errors during PR creation or an excessive number of small patch branches clutter the repository. Remedies: scope bot permissions to the minimum necessary, add a branch cleanup policy for auto-generated branches older than a threshold, and limit concurrent open bot PRs per repo to prevent overload.
Review artifacts not auditable
Symptoms: missing JSON output, absent links between review and PR, or ephemeral logs. Remedies: persist review artifacts to a durable object store referenced from the PR; attach the artifact path in the PR body and the associated issue ticket. Use immutable naming conventions for review artifacts (include finding ID, timestamp, commit SHA).
Conclusion
Remediation workflows are operational playbooks: they must be conservative, auditable, and measurable. Use the @codex fix the P1 issue capability to reduce developer toil for low-risk changes while keeping humans in the loop for judgment calls. Assign clear rule ownership with SLAs and escalation paths, instrument everything for metrics-driven decisions, and advance through phased rollout stages to avoid surprise regressions.
Following the remediation checklist and the troubleshooting guidance above will help your organization maintain high signal-to-noise in automated reviews, build trust in automated remediation, and ensure every Codex finding becomes a traceable, testable change or an accepted exception.
Within How to Create Custom Code Review Rules for Codex with AGENTS.md: Complete Repository Governance Playbook, the Designing high-signal P0/P1 rules decision connects directly to Codex CLI Prompts Masterclass: 40 Advanced Prompts for Multi-Agent Development, Code Review, and CI/CD Automation. That linked article specifically examines codex CLI Prompts Masterclass: 40 Advanced Prompts for Multi-Agent Development, Code Review, and CI/CD Automation, giving teams concrete background for applying the present article’s Designing high-signal P0/P1 rules recommendations without duplicating this workflow’s scope.
