
Govern Shared Codex Cloud Environments: Publish Setup, Separate Personal Secrets, Limit Domain Access, and Control Task State
Evidence checkpoints
Documented point: Publishing captures a prepared filesystem for new Cloud tasks; an existing task retains its own saved files, including uncommitted changes and installed tools. Saving configuration differs from publishing a reusable setup; commit important work to source control. [official source 1 official source 2]
Documented point: OpenAI Cloud documentation distinguishes direct environment variables, network secrets substituted by proxy over Hypertext Transfer Protocol Secure (HTTPS)The encrypted form of web communication protected with Transport Layer Security. Open glossary entry on port 443, and Personal vault values that belong to individual users. Variables reach programs directly; network-secret behaviour is limited to documented proxy substitution and allowed destinations; requested environment-specific personal values override general defaults. [official source 1]
Documented point: Enterprise environment sharing shares prepared setup and requirements, not another person’s task, personal credentials, repository permissions, or personal connections. Review prepared files, environment-owned credentials, cloud identities, and virtual private network (VPN)A protected logical connection that carries traffic across another network. Open glossary entry connections before sharing; source-system authorisation remains account-dependent. [official source 1 official source 2]
Documented point: Republishing changes the reusable setup for new tasks, while existing tasks retain their state; saved virtual machine (VM)A software-defined computing environment that runs an operating system and applications. Open glossary entry state is documented as recoverable for up to seven days after the last start or resume. The seven days concern VM recovery, not chat retention, backup or archival guarantees. [official source 1 official source 2]
Documented point: Destination settings and Enterprise Agent Security are separate layers: an Agent Security allowed domain does not override an environment restriction. Allowlisting supplies neither credentials nor service authorisation; test allow/block behaviour after configuration and policy changes. [official source 1 official source 2 official source 3]
Start with the correct mental model: an environment is a reusable starting point, not a shared task
OpenAI’s Codex Cloud documentation distinguishes the reusable cloud environment from the task workspace created from it. A prepared and published environment provides a filesystem and configuration from which authorised users can start new Cloud tasks. Each new task then receives its own workspace. Publishing does not turn the owner’s current task into a collaborative task, expose another user’s task history, or merge teammates into one shared virtual machine.
This distinction controls nearly every governance decision in this guide. Treat the published environment as a governed template and each task as a separate working instance. The template can contain prepared files, installed tools and other reusable setup. The task can subsequently accumulate its own files, installed software and uncommitted changes. Once those states diverge, editing or republishing the template does not rewrite the task.
Operational rule: publish what every authorised future task should start with; commit what the organisation must preserve; keep task-specific experiments inside the task; and never assume republishing will repair, update or recover an already-created task.
“Shared environment” is therefore shorthand for shared reusable setup, not shared task state. According to OpenAI, Enterprise environment sharing can make prepared setup and requirements available to authorised teammates. It does not transfer another person’s task, Personal vault values, repository permissions or personal connections. Source-system access continues to depend on the account and authorisation of the user starting the task.
The same separation applies to credentials. An environment-owned credential or connection belongs to the reusable environment’s configuration and may become usable by authorised teammates through that environment. A Personal vault value belongs to an individual user. It is not converted into an environment-owned value merely because a task requests it. Before publication or sharing, owners must identify which files, identities, credentials and connections are reusable organisational resources and which must remain user-specific.
For ChatGPT Work and Codex defaults, roles, reasoning settings, and local or cloud access, see Configure ChatGPT Work and Codex Starting Defaults: Models, Reasoning, Fast Mode, Roles, Local Access, and Cloud Access.
The lifecycle: design, test, publish, share, republish and retire
A controlled environment lifecycle has six operating phases. “Save” sits within design and maintenance, while “new task” and “existing task” describe the two state paths administrators must test after publication. The phases should be recorded separately because each action affects a different object and audience.
| Lifecycle action | Object affected | Who sees the effect | What it does not establish |
|---|---|---|---|
| Design | Draft environment configuration and prepared filesystem | Environment owner and authorised maintainers | Readiness for general use |
| Save | Current environment configuration or preparation work | Depends on the current product surface and permissions | A published reusable baseline for future tasks |
| Test | A controlled task or validation instance | Testers with the required Cloud and source-system access | Universal success for every user, repository or destination |
| Publish | Reusable prepared filesystem and associated environment setup | Authorised users of the published environment | A shared task, transferred repository permission or personal credential |
| Share | Availability of the published environment | Eligible and authorised teammates | Access to another person’s task or external systems |
| Republish | Reusable baseline for later new tasks | Users who start tasks from the revised publication | Mutation of tasks that already exist |
| Retire | Use of the environment as an approved starting point | Prospective users and environment maintainers | Automatic archival, backup or deletion of all related task state |
1. Design the reusable boundary
Design begins by deciding what belongs in the common starting filesystem. Suitable candidates include project scaffolding, dependency declarations, tool configuration, non-sensitive fixtures and documented setup scripts. Files that contain personal credentials, unreviewed exports, production data or task-specific work should not be included merely because they are convenient during preparation.
Recommended governance procedure: maintain an environment manifest that names the environment owner, intended repositories, permitted user population, prepared files, installed tools, external destinations, credential classes, test cases and retirement condition. This is a recommended control template, not an OpenAI-required format. Its purpose is to make the publication decision reviewable rather than relying on the preparer’s memory.
Classify every credential or runtime value before configuring it. OpenAI’s Cloud environment documentation distinguishes direct environment variables, network secrets used through documented HTTPS port 443 proxy substitution, and individual Personal vault values. These delivery paths have different ownership and exposure characteristics; they should not be grouped under an undifferentiated “secrets” label.
Direct environment variables reach programs in the task environment. Owners should therefore assume that task processes capable of reading those variables may use them. Network secrets follow the proxy-substitution behaviour documented by OpenAI and are tied to allowed destinations; that mechanism should not be generalised into a claim that the value is inaccessible in every circumstance. Personal vault values are stored per user, with requested environment-specific personal values overriding general defaults where the documented matching behaviour applies.
Design also needs a source-control decision. The prepared filesystem may improve startup consistency, but it is not a substitute for a repository. Project code, dependency manifests, configuration intended for review and other durable artefacts should normally be committed to the organisation’s authorised source-control system. That preserves history, enables review and avoids making a published virtual-machine image the only copy of important work.
2. Save preparation without confusing save and publish
OpenAI distinguishes saving environment configuration from publishing a reusable setup. Saving preserves preparation or configuration in its applicable context; publishing captures the prepared filesystem for new Cloud tasks. An owner should not announce an environment as ready merely because the latest edits were saved.
Decision rule: if another authorised user must be able to create a fresh task that starts from the prepared filesystem, the owner must complete the documented publication flow rather than relying on a saved draft. Conversely, if preparation is incomplete or contains material that has not passed review, save it for further work but do not publish it as the approved baseline.
Before publication, inspect the filesystem rather than reviewing configuration fields alone. Prepared files can disclose internal endpoints, test data, package configuration, shell history or helper scripts. Sharing may also expose environment-owned credentials, cloud identities or VPN connections to authorised teammates. A review that checks only the environment name and domain list will miss these material sharing boundaries.
3. Test both the setup and the authorisation boundaries
Testing should use a newly created task because publication governs the starting state of new tasks. A task that was created before the latest preparation may contain cached tools, files or uncommitted fixes that make the environment appear healthier than the published baseline. Validation in an old task can therefore produce a false result.
Recommended test protocol: create a fresh task using a non-production repository or other approved test target; confirm expected files and tools; verify dependency installation or startup checks; test an intended destination; test a destination that should be blocked; confirm that a user without source-system permission does not gain that permission through the environment; and verify that Personal vault requirements are resolved per user rather than inherited from the owner.
Use test identities representing relevant permission classes where organisational policy allows it. The environment owner’s successful test proves only that the owner’s combination of workspace access, repository rights, personal connections and credentials worked. It does not prove that every authorised teammate has equivalent source-system access.
Network tests must examine control layering. OpenAI documents environment internet settings and Enterprise Agent Security as separate layers. An Agent Security allowed domain does not override an environment restriction. Equally, a domain permitted at both layers does not provide credentials or establish that the task is authorised to call the service. Test the effective allow and block behaviour after changes to either layer.
For auditable Codex approval policies for controlling agent autonomy, see The Complete Guide to Codex Approval Policies — Controlling AI Autonomy in Enterprise Environments.
Sandboxing, approval policies, destination restrictions and Agent Security should be treated as complementary controls, not interchangeable assurances. OpenAI’s documentation describes these as separate layers. A permissive result in one layer cannot be used to infer that the other layers have approved the operation, and none removes the need to review credentials, data scope and external-service authorisation.
4. Publish an identified baseline
Publishing should be a named release event rather than an informal action at the end of preparation. Record the publication date, owner, source revision where applicable, dependency state, approved destinations, credential classes and validation result. If the product surface does not provide every desired metadata field, maintain the record in an authorised change-management system.
OpenAI says publishing captures a prepared filesystem for new Cloud tasks. The practical implication is that publication creates a starting baseline, not a continuously synchronised environment. After a task starts, its workspace can diverge through generated files, installed tools, dependency updates and uncommitted edits.
Recommended naming convention: use a stable project identifier plus a publication date or internal release identifier, such as payments-service / baseline 2026-09-30. This is an example, not a documented Codex requirement. Avoid names such as “latest” or “final” unless an external register resolves them to a specific reviewed publication.
Publication approval should include a credential-owner check. For each configured value or connection, record whether it is environment-owned, user-owned through Personal vault, or supplied through another authorised account-dependent connection. If ownership cannot be established, remove the value from the publication until a responsible owner and rotation process are identified.
5. Share the environment, not the owner’s authority
In the Enterprise context described by OpenAI, sharing makes prepared setup and requirements available to authorised teammates. It does not clone the environment owner’s repository permission, personal credentials, personal connections or task. Every teammate remains subject to their own account permissions in the source system and to applicable workspace controls.
This produces a useful access equation:
Effective task access =
workspace entitlement
∩ Cloud permission
∩ environment availability
∩ repository or source-system permission
∩ destination policy
∩ available credential or personal connection
∩ applicable sandbox and approval controls
The formula is a recommended governance model, not an OpenAI product specification. The intersection symbol is deliberate: access generally fails when a required layer is absent. Environment sharing must not be treated as a union that fills missing repository rights or service authorisation.
Consider an environment prepared for two repositories and an internal package service. A teammate may see and start the environment but have permission to only one repository. Sharing the environment does not grant access to the second repository. If the package service requires a Personal vault value, the teammate must provide their own appropriate value; they do not inherit the preparer’s personal value. If an environment-owned credential is deliberately configured for shared use, its scope and authorised user population require separate review.
Owners should communicate these limits in the environment description or associated runbook. State which setup is shared, which personal values users must supply, which repositories require independent permission, which destinations are expected, and who handles failed-access requests. This prevents users from remediating an authorisation failure by adding broader credentials to the shared environment.
6. Separate the new-task path from the existing-task path
After publication, governance divides into two paths. A new task starts from the currently published reusable setup available to that user. An existing task retains its own saved files, including installed tools and uncommitted changes, according to OpenAI’s documentation. That existing state is not replaced merely because the environment is edited or republished.
| Question | New task | Existing task |
|---|---|---|
| Which reusable setup applies? | The publication available when the task is created | The task already has its own workspace state |
| Does a later republish rewrite it? | Not applicable until another task is created | No |
| Can it contain uncommitted changes? | Not from another task | Yes, if created in that task |
| Should it hold the only durable copy of important work? | No | No; commit important work to source control |
This distinction matters during incident response. If a published setup contains an unsafe package, obsolete certificate or over-broad credential, republishing a corrected baseline protects future task creation only. Administrators must separately identify active existing tasks and decide whether users should stop, migrate, rotate credentials, commit safe work or create replacement tasks. Republishing alone is not remediation for already-instantiated workspaces.
It also matters during support. When two users report different behaviour, first establish whether they started tasks before or after the relevant publication. Then compare each user’s repository rights, Personal vault configuration, connections and task-local changes. Treating both tasks as identical because they show the same environment name can conceal the real cause.
7. Republish for future tasks with an explicit migration notice
Republishing updates the reusable setup used by future tasks; it does not mutate existing tasks. The owner should therefore classify every republish as either backward-compatible, migration-required or urgent replacement. This classification is a recommended practice and should be based on the effect on users, credentials and source compatibility.
- Backward-compatible: future tasks gain a reviewed tool or non-breaking configuration while existing tasks can continue safely.
- Migration-required: future tasks use a changed dependency, filesystem layout or setup process, and existing task owners need instructions for moving work.
- Urgent replacement: an exposed credential, prohibited file, unsafe connection or materially defective baseline requires administrators to stop recommending the old state and coordinate human-led remediation.
A migration notice should identify the old publication, new publication, reason for change, affected users, required source-control actions and credential implications. It should say explicitly that existing tasks do not update automatically. If users must create new tasks, instruct them to commit or otherwise preserve authorised work first; do not imply that a new task can recover another task’s uncommitted files.
Credential changes require particular care. Rotating an environment-owned credential in a republished setup does not prove that every existing task has stopped using the previous credential. Follow the credential provider’s authorised rotation and revocation process, investigate scope and logs as organisational policy requires, and do not rely on republishing as the revocation mechanism.
8. Retire deliberately rather than abandoning an environment
Retirement means the environment should no longer be used as an approved starting point. Trigger conditions can include project closure, repository archival, unsupported dependencies, ownership loss, superseding publication, connection changes or inability to validate the configuration. Retirement is a governance action; it should not be inferred from inactivity alone.
Recommended retirement checklist: identify a successor where one exists; notify authorised users; prevent new use through available controls; remove or rotate environment-owned credentials; disconnect obsolete identities or VPN connections; preserve required configuration records; and review outstanding tasks separately. Product labels and available management actions can vary by plan, workspace setting and rollout, so verify the current interface and OpenAI documentation before acting.
Do not describe retirement as deletion, archival or guaranteed purge unless the applicable product documentation and organisational evidence support that specific action. Existing tasks and external credentials may have separate lifecycles. Source-control records, audit evidence and connected-service access must be governed in their respective systems.
Assign ownership across workspace, environment, credentials and tasks
No single “admin” label should be assumed to carry every relevant authority. OpenAI’s Enterprise administration documentation separates workspace controls, Cloud use, workspace environment management, local runtime, connected systems and reporting. Current labels and permissions can vary, so organisations should map responsibilities to the controls visible in their own workspace rather than relying on generic role names.
| Governance role | Primary responsibility | Boundary |
|---|---|---|
| Workspace administrator | Controls workspace-level eligibility and relevant Cloud or environment-management permissions | Does not automatically own repositories, credentials or each task |
| Environment owner | Designs, tests, publishes, documents, republishes and retires the reusable setup | Cannot grant source-system rights merely by sharing the environment |
| Credential owner | Approves scope, storage path, rotation, revocation and authorised users for an environment-owned credential | Must not assume a domain allowlist provides authorisation |
| Repository or service owner | Grants and reviews access in the source system | Permission remains account-dependent and external to environment publication |
| Task user | Starts authorised tasks, supplies personal values where required, reviews changes and preserves important work | Must not treat task state as durable source control or backup |
| Security or risk reviewer | Reviews control layering, destinations, data scope and incident procedures | This review does not turn product configuration into a compliance guarantee |
One person may hold several roles, particularly in a small team, but the decisions remain distinct. The person authorised to publish a filesystem may not be authorised to create a broadly shared service credential. The person who owns a repository may not administer the Codex workspace. Record the approval for each boundary instead of treating organisational seniority as universal technical authority.
Apply plan, workspace and health-data qualifiers before rollout
Codex Cloud access, interface labels, roles and controls can depend on plan, workspace configuration, rollout status and individual authorisation. Before implementing this lifecycle, confirm that the intended users can use Codex Cloud and that designated administrators can manage workspace environments where required. Do not promise feature parity or availability based solely on another workspace’s interface.
Revalidate the product surface when procedures are executed, not only when they are written. OpenAI documentation was reviewed for this guide on 30 September 2026, but product controls can change. A runbook should direct operators to compare current documentation and in-product permissions before publishing, sharing, republishing or retiring an environment.
OpenAI states that Codex Cloud is not covered by the OpenAI business associate agreement (BAA)A contract that establishes required safeguards and responsibilities when a covered entity or business associate handles protected health information. Open glossary entry. Under the cited guidance, do not process protected health information (PHI)Individually identifiable health information protected under applicable United States health-information rules. Open glossary entry in Codex Cloud. This is a product-boundary warning, not legal advice; organisations should route health-data decisions through their authorised privacy, legal and security functions.
Keep source control and recovery claims narrow
OpenAI’s Help Center describes saved VM state as recoverable for up to seven days after the task was last started or resumed. The seven-day statement concerns recovery of saved VM state. It is not a promise of chat retention, long-term storage, backup, archival, disaster recovery or recovery of another task’s uncommitted work.
The safe operating rule is to commit important work to an authorised source-control repository before relying on task closure, migration or retirement. Where material should not enter source control, preserve it through an organisation-approved records or artefact process. A saved VM can support short-term continuity, but it should not become the only copy of consequential work.
This guide is a documented configuration-and-governance procedure, not a security assessment, penetration test or compliance guarantee. The mental model is intentionally conservative: publication governs future starting state; sharing governs environment availability; external permissions remain external; personal credentials remain personal; existing tasks retain their own state; and durable work belongs in an authorised system of record.
Choose credential delivery by ownership, exposure path and destination
OpenAI’s Codex Cloud documentation describes three distinct credential mechanisms: direct environment variables, network secrets and Personal vault values. OpenAI’s Cloud environment documentation distinguishes them by how a value reaches a task, who owns it and, for network secrets, where proxy substitution may occur. Treating the three as interchangeable can either expose a credential more broadly than intended or leave a shared environment unusable for teammates.
The governing decision should begin with ownership rather than convenience. If a credential belongs to the reusable environment and is intentionally available to every authorised user of that environment, it may be an environment-owned value. If each person must act through an individual account or identity, request a Personal vault value instead. If a secret only needs to be inserted into an eligible outbound HTTPS request on port 443 to an approved destination, assess whether a network secret is the narrower documented delivery path.
For preventive Codex managed configuration compared with runtime detection, see Falcon Guardian vs Codex Managed Configuration: Runtime Detection vs Preventive Agent Controls.
Do not select a mechanism merely because an application expects a familiar variable name. The application’s consumption pattern, the destination protocol, the source system’s authorisation model and the consequences of sharing must all agree. An environment variable is directly available to programs; a network secret depends on documented proxy substitution and destination controls; a Personal vault value remains owned by the individual user even when an environment requests it.
Decision table: direct variables, network secrets and Personal vault
| Decision factor | Direct environment variable | Network secret | Personal vault value |
|---|---|---|---|
| Primary purpose | Supply configuration or a credential directly to programs running in the task environment. | Support documented proxy substitution of a secret into eligible outbound HTTPS traffic on port 443. | Let an individual user supply a personal value requested by the environment without transferring another user’s value. |
| Delivery path | The value reaches programs directly as an environment variable. Code, tools and subprocesses able to read the task environment may therefore be able to access it. | The documented mechanism substitutes the secret through the network proxy for requests to configured destinations. It is not a general-purpose variable-delivery mechanism. | The user’s value is supplied for that user’s task according to the environment’s request. OpenAI documents that an environment-specific personal value overrides a general default when both apply. |
| Typical ownership model | Usually environment-owned when configured as part of reusable shared setup, although non-secret configuration may also use variables. | Usually environment-owned when the shared environment requires a common service credential for a narrowly defined destination. | Individual-user owned. Each authorised teammate supplies and maintains their own value. |
| Effect of sharing the environment | Authorised teammates may receive the prepared setup together with environment-owned values. Review this exposure before sharing. | Authorised teammates may be able to use the environment-owned connection path for configured destinations. Sharing does not make the remote service authorise every operation. | The owner’s personal value is not transferred. Each teammate must provide their own required value and retain their own source-system authorisation. |
| Destination allowlist relationship | A variable does not itself permit network access. Environment destination settings and other policy layers still apply. | The destination restriction is integral to the documented substitution model. Configure only the required destination and test both permitted and rejected traffic. | A personal credential does not open a destination. The environment and workspace must still permit the required network route. |
| Service authorisation | Possession of the value does not prove that the task, user or intended operation is authorised by the service. | Allowlisting and substitution do not confer service permissions. The target system still evaluates the supplied credential and its scopes. | The source service determines what the individual account may do. Environment sharing does not clone or elevate those permissions. |
| Best fit | A program genuinely requires direct variable access and the owner accepts that task programs can receive the value. | A supported HTTPS integration needs a secret only at a defined outbound destination and does not require direct program access in another form. | Actions must remain attributable to, or authorised through, each user’s own account or connection. |
| Poor fit | A high-impact credential that should never be visible to task programs, or a personal credential that should not be shared with teammates. | Non-HTTPS traffic, traffic outside port 443, arbitrary shell use of a secret, or a service pattern not covered by documented proxy substitution. | A deliberately shared machine identity whose lifecycle belongs to the environment owner rather than individual users. |
| Rotation responsibility | The environment credential owner rotates the source credential, updates the environment and validates future tasks. | The environment credential owner rotates the secret, confirms destination matching and retests substitution without logging the value. | Each user rotates or revokes their own value. The environment owner maintains only the request and usage contract. |
| Offboarding effect | Removing a user from the shared environment does not by itself rotate an environment-owned credential that the user may previously have been able to use. | Access removal and credential rotation are separate controls. Review whether offboarding requires rotation or source-service revocation. | Revoke the departing user’s source-system credential or connection under that system’s process; other users’ vault values remain separate. |
| Required validation | Confirm the intended program can read the value, unintended scripts do not print it, and blocked destinations remain blocked. | Confirm substitution occurs only for the intended destination and that near-match, alternate-domain and disallowed requests fail safely. | Test with at least two authorised users so that success cannot be explained by the environment owner’s personal connection or repository access. |
Decision rule: prefer the mechanism with the narrowest delivery path that still satisfies the application contract. Use a direct variable only when the program must receive the value directly. Consider a network secret only for the documented HTTPS-on-port-443 proxy-substitution case and an explicitly permitted destination. Use Personal vault when the credential must remain attached to each user rather than to the shared environment.
Operational warning: “personal” describes ownership, not an assurance that a value can never become visible during task execution. A task may pass a supplied value to authorised tools or services, and unsafe scripts may print, persist or misuse task-visible material. Minimise scope, avoid diagnostic output containing secrets, review task instructions and validate the consuming code before enabling other users.
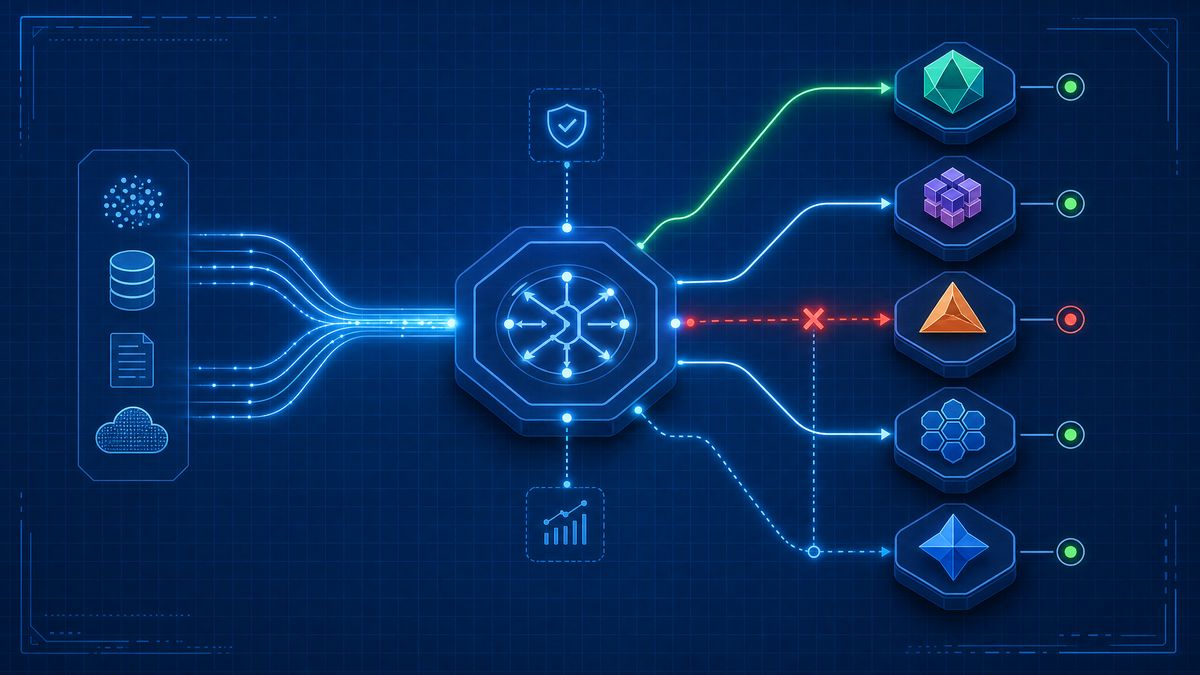
Map the complete delivery chain before adding a secret
A credential review should document the full chain rather than recording only the field in which a value is entered. The chain begins with the credential owner, passes through a Codex delivery mechanism, reaches either a program or the network proxy, and terminates at a named service that makes its own authorisation decision. Each step has a separate control question.
- Name the owner. Record whether the credential belongs to the environment, an individual user or an external platform team. Do not use a personal credential as an undocumented shared machine identity.
- Name the consumer. Identify the exact program, package manager, command or remote service that needs the value. “Build tooling” is too broad to support a least-exposure decision.
- Specify delivery. State whether the program must read a variable directly or whether proxy substitution into an eligible HTTPS request is sufficient. For Personal vault, identify the requested personal value without pre-populating another user’s credential.
- Define the destination. Record the required domain and purpose. Do not approve broad destination patterns merely to avoid investigating the dependency chain.
- Define source-system scope. In the remote service, restrict the credential to the repositories, projects, operations or resources needed for the workflow where that service supports such controls.
- Define failure behaviour. A missing personal value, blocked domain or rejected remote authorisation should stop the relevant operation clearly. It should not trigger a fallback to a broader shared credential.
- Define rotation and revocation. Assign a human owner, review event and offboarding response. Publishing or republishing an environment is not a substitute for revoking a credential at its source.
Recommended credential record: maintain the environment name and version, credential owner, delivery mechanism, consuming command, permitted destination, source-system scope, rotation owner, last validation date and retirement condition. Store references or identifiers rather than secret values in the governance record.
Environment: project-build-baseline
Credential class: personal
Requested value: package_registry_token
Consumer: dependency installation command
Destination: approved package registry domain
Source authority: each user's registry account
Failure rule: stop installation; no shared-token fallback
Rotation owner: individual user
Environment review owner: platform team
Secret value recorded here: no
The example is a governance template, not a prescribed product configuration. Names should be generic enough to avoid disclosing a credential, while still making ownership and purpose unambiguous. Never place an actual token, certificate, private key or connection string in a ticket, source repository, screenshot or environment description.
Separate environment-owned credentials from personal authority
An environment-owned credential is part of the reusable operating boundary. If authorised teammates can use the published environment, they may be able to benefit from that credential or connection. This may be appropriate for a narrowly scoped shared service identity, but it must be an explicit administrative decision rather than an accidental consequence of publishing setup.
Personal vault supports a different model. OpenAI describes it as individual-user storage, with requested environment-specific personal values taking precedence over general defaults. The environment can declare that a personal value is needed, but the publisher’s value does not become the teammate’s value. This separation is important where the source service audits actions by user, applies account-specific permissions or requires individual revocation.
Recommendation: test a shared environment with a second authorised account that has only its intended repository and service permissions. If the second user succeeds without supplying the required personal value, investigate whether an environment-owned credential, prepared file, active connection or fallback identity is supplying unintended authority.
A successful test by the environment owner proves little about teammate access. The owner may have broader repository permission, a personal connection, a previously configured vault value or access to a cloud identity unavailable to others. Use separate test identities to distinguish correct reusable setup from authority inherited only by the owner.
Environment sharing distributes prepared setup and declared requirements. It does not transfer another person’s Personal vault values, task workspace, repository permissions or personal connections.
Review prepared files and connections as credential material
Secrets are not confined to fields labelled “secret”. Before publishing or sharing, inspect the prepared filesystem for configuration files, command histories, cached authentication artefacts, package-manager files, cloud profiles, private keys, generated credentials and copied diagnostic output. OpenAI’s documentation warns administrators to review prepared files, environment-owned credentials, cloud identities and VPN connections when sharing environments.
Recommended review procedure: search by file type and location, then inspect the setup process that created each file. Do not rely solely on string matching for words such as “token” or “password”; credentials may use opaque names or binary stores. Remove personal material, rebuild the preparation process with non-secret placeholders where possible, then publish from the cleaned baseline.
- Check home-directory configuration and cache locations created by setup commands.
- Inspect repository-adjacent files excluded from version control, because exclusion does not prevent inclusion in a prepared filesystem.
- Review shell startup files and scripts for embedded values, credential-export commands and logging.
- Confirm that package installation did not preserve a personal registry credential in a configuration file.
- Review cloud and VPN configuration for identities or routes that should not become reusable.
- Remove generated logs containing request headers, signed addresses, cookies or connection diagnostics.
- Re-run the setup from a clean state and verify that it requests credentials through the intended mechanism.
Do not assume that deleting a credential from the current preparation session resolves every exposure. If the value was committed to source control, transmitted to a service, included in a published baseline or disclosed in logs, follow the owning system’s incident and rotation process. Republishing a cleaned environment affects the reusable setup for future tasks; it does not revoke the original credential or rewrite existing task state.
Use destination controls as one layer, not as authorisation
A destination allowlist answers a network-routing question: may traffic target this destination under the configured controls? It does not answer whether the user is entitled to access the service, whether the credential has suitable scope, whether the requested operation is approved or whether data sent in the request is appropriate.
OpenAI documents environment internet settings and Enterprise Agent Security as separate layers. An allowed domain in Agent Security does not override a more restrictive environment setting. Conversely, permitting a destination at the environment layer does not grant a credential, repository permission or remote-service role. Administrators must align both layers and then test their combined effect.
For Codex sandbox and network rules for secure development, see How to Configure Codex Auto-Review Mode and Sandbox Rules for Secure AI-Assisted Development.
Build a destination matrix before permitting outbound access
Recommended method: maintain a destination matrix that links each permitted domain to a business purpose, delivery mechanism, credential owner and negative test. This prevents a broad allowlist from becoming an undocumented substitute for service design.
| Matrix field | Required entry | Review question |
|---|---|---|
| Destination | The precise domain required by the integration. | Is this the actual service endpoint rather than an unnecessarily broad parent domain? |
| Purpose | A concrete operation such as retrieving approved dependencies or reading an authorised repository. | Would a reviewer understand why the task needs this route? |
| Protocol constraint | The protocol and port expected by the documented integration. | If using a network secret, does the design stay within documented HTTPS port 443 substitution? |
| Credential class | None, environment-owned variable, environment-owned network secret or Personal vault. | Does ownership match the service’s accountability model? |
| Remote permission | The source-system role or scope expected for the credential. | Is the remote permission narrower than the user’s or service account’s general access? |
| Positive test | An approved, non-destructive request expected to succeed. | Does success demonstrate the intended route without making a consequential change? |
| Negative test | A disallowed destination, missing credential or unauthorised resource expected to fail. | Does failure occur at the expected layer without revealing secret material? |
| Review trigger | Credential rotation, domain change, policy change, ownership change or environment republish. | Who must revalidate the route before future use? |
Positive testing alone is insufficient because a request may succeed through an unintended route or broader identity. Test a permitted destination with the expected credential, the same destination without that credential, an unauthorised resource at the permitted service and a nearby but unapproved destination. Use harmless requests and avoid testing against production-changing operations.
Operational warning: do not infer that a blocked request proves a secret is protected from every form of disclosure. A direct environment variable may still be readable by programs, and task output or files may expose values independently of network policy. Likewise, do not claim that network secrets are universally inaccessible; limit conclusions to the documented substitution behaviour and the tests actually performed.
What sharing does and does not transfer
For Enterprise environment sharing, OpenAI distinguishes the reusable prepared environment from each user’s task and external authority. Sharing can make prepared files and environment-owned credentials or connections available to authorised teammates. It does not share another person’s task, Personal vault values, repository permissions or personal service connections.
| Item | Transferred by environment sharing? | Required administrative action |
|---|---|---|
| Prepared filesystem | It can form the reusable starting point for authorised users’ new Cloud tasks. | Inspect files and generated state before publication and after setup changes. |
| Environment-owned variable or network secret | It may become usable through the shared environment according to its configured delivery path. | Confirm that shared ownership is intended, scope the credential and assign rotation. |
| Publisher’s Personal vault value | No. Personal values remain per user. | Require each teammate to provide their own value where the environment requests it. |
| Publisher’s task workspace | No. A published environment is not the publisher’s task. | Use source control or another approved collaboration process for work that must be shared. |
| Uncommitted changes in another task | No. Existing tasks retain their own saved files and state. | Commit important work to source control; do not use publishing as backup or task migration. |
| Repository permission | No. Sharing does not clone or bypass repository authorisation. | Grant and review repository access in the source system through its authorised process. |
| Personal connection | No. A teammate does not inherit the publisher’s personal connection. | Configure individual connections or an explicitly approved environment-owned identity. |
| Remote service authorisation | No. The target service continues to evaluate the account or credential presented. | Apply least privilege and validate access independently for each user or shared identity. |
This distinction should shape onboarding instructions. Tell users which setup is already present, which Personal vault values they must provide, which repository access they must obtain separately and which destinations are permitted. Do not describe the environment as “fully configured” if successful use still depends on personal permissions or connections.
Apply a publish-time boundary check
Recommended release gate: before sharing or republishing, require the environment owner and a separate authorised reviewer to answer the following questions. A “no” or “unknown” answer should block publication until the ownership or delivery path is resolved.
- Can every environment-owned credential be linked to a named owner, purpose, destination and rotation process?
- Have all credentials that should remain user-specific been represented as Personal vault requirements rather than publisher-owned values?
- Have prepared files, caches, histories, cloud profiles and VPN configuration been reviewed for personal or over-broad authority?
- Does each network secret stay within the documented HTTPS port 443 substitution case?
- Are environment destination settings and Agent Security rules aligned without assuming one overrides the other?
- Has a second authorised user tested the environment with different repository and service permissions?
- Have both allowed and blocked network behaviours been tested after the latest policy change?
- Does the user documentation state that sharing does not transfer tasks, Personal vault values, repository permissions or personal connections?
- Is important code and configuration committed to source control rather than left only in task state?
- Is there a retirement plan for credentials, destinations and the published environment?
Republishing after a credential or destination change updates the reusable setup for new tasks; it does not alter tasks that already exist. Existing tasks retain their own files, including installed tools and uncommitted changes. Where a credential must be revoked urgently, revoke it in the source system first, assess affected existing tasks and then update and republish the environment for future tasks.
OpenAI documents saved VM state as recoverable for up to seven days after the task was last started or resumed. That qualifier is about VM recovery, not a promise of chat retention, archival storage, backup or recovery of another user’s work. Commit important work to source control and use approved organisational backup and records processes.
Codex Cloud availability, labels, permissions and controls can vary by plan, workspace configuration, rollout and user authorisation. OpenAI’s administrator documentation also distinguishes permission to use Codex Cloud from permission to manage workspace environments. Verify the live product surface and assign only authorised owners before applying this workflow.
OpenAI states that Codex Cloud is not covered by its business associate agreement, so protected health information must not be processed in these environments. Credential and network configuration remains subject to the organisation’s security, privacy, legal and procurement review.
Official source checkpoints
- OpenAI Codex documentation: Cloud environments — saving, publishing, variables, network secrets, Personal vault, sharing and task state; accessed 30 September 2026.
- OpenAI Help Center: Using Codex Cloud — prepared environments, task workspaces, saved VM recovery and the BAA boundary; dated 30 September 2026.
- OpenAI Codex documentation: Admin rollout guide — workspace, Cloud and environment-management permissions; accessed 30 September 2026.
- OpenAI Codex documentation: Agent approvals and security — separate sandbox, approval, Agent Security and environment internet-control layers; accessed 30 September 2026.
Control task state, source permissions and policy as separate boundaries
OpenAI’s Codex Cloud documentation separates the reusable environment from the workspace created for each task. That distinction determines what a teammate receives, what republishing changes, and where uncommitted work remains. A published environment supplies a prepared starting filesystem for new tasks; it does not turn all tasks into one shared machine or expose another user’s task history and working directory.
Administrators should therefore govern four objects independently: the published environment baseline, each task workspace, the user’s repository permissions, and the workspace-level policy controls. Treating any one of these as evidence for another creates unsafe assumptions. For example, being allowed to select an environment does not establish repository access, and being able to reach a domain does not establish permission to use the service behind it.
Operational rule: publish reusable preparation, commit durable project work to source control, and evaluate every user and task against its own repository, credential, connection and policy context.
Model each task as an independent working copy
According to OpenAI’s Cloud documentation and Help Center guidance, tasks launched from the same environment have separate workspaces. The published filesystem is their common starting point, but subsequent files, installed tools and uncommitted changes belong to the individual task state. One task cannot be treated as a live continuation of another merely because both display the same environment name.
This boundary matters during collaboration. Sharing an Enterprise environment makes its prepared setup and declared requirements reusable by authorised teammates. It does not share the environment owner’s existing task, transfer the owner’s uncommitted edits, or make one teammate’s task-visible files appear in another teammate’s workspace. If work must pass between people, use the organisation’s approved source-control and artefact-transfer process rather than relying on environment sharing.
Recommended task hand-off procedure:
- Identify the exact task whose work is being handed over.
- Inspect its working tree and distinguish tracked, modified, untracked and ignored files.
- Remove generated files, credentials, tokens, local caches and other material that must not enter source control.
- Run the project’s approved checks and record their results.
- Commit the intended changes to an authorised branch or produce an approved review artefact.
- Have the receiving user obtain the work through the repository or approved artefact system.
- Start a separate task from the appropriate published environment and verify the checked-out revision.
This procedure is a governance recommendation, not a claim that Codex automatically performs or validates the hand-off. A repository commit preserves reviewed project changes more reliably than an assumption about recoverable virtual-machine state, but source control is not itself a backup for every generated file or external dependency. Apply the organisation’s separate backup and records policies where required.
For persistent Codex Cloud environments and long-running workflows, see OpenAI Acquires Ona: How Persistent Cloud Environments Will Transform Codex for Enterprise.
Distinguish republishing from updating a running task
OpenAI documents republishing as a change to the reusable setup used by new tasks. Existing tasks retain their own saved files, which can include uncommitted changes and tools installed after the task began. Republishing does not rewrite an existing task’s filesystem, inject a newly installed dependency into it, or migrate its working tree to the new baseline.
The practical consequence is that two tasks associated with the same named environment can run against different preparation states. A task started before republishing can retain the earlier baseline plus its local modifications, while a task started afterwards can receive the republished baseline. Environment owners should record a baseline identifier in a non-secret file so users can identify which preparation state a task received.
Recommended baseline record: place a small, non-sensitive manifest in the prepared filesystem containing an internal environment revision, publication date, expected repository or project identifier, supported setup-script revision and owner contact. Do not put credentials, private connection strings or personal identifiers in this file. The manifest is an operational aid rather than proof that every dependency or policy matches the recorded values.
| Change or event | Existing task | New task after publication | Required administrative response |
|---|---|---|---|
| Tool is added and the environment is republished | Retains its existing tools and files; do not assume the new tool appears | Receives the republished prepared filesystem | Tell existing-task owners whether to continue, install the approved tool separately, or start a replacement task |
| Prepared configuration file is corrected | Keeps its task-local copy unless deliberately changed | Starts with the corrected published copy | Assess whether the defect is operational or security-relevant and issue an explicit migration instruction |
| Environment-owned credential is rotated | Behaviour depends on the credential delivery path and task context; verify rather than infer | Must be tested against the current authorised credential configuration | Revoke the old credential at its authoritative service, review active tasks and test both permitted and denied requests |
| Repository permissions change | User access remains subject to the repository provider and current account authorisation | Environment sharing does not grant access | Validate access with the affected user account and remove stale sessions or connections under the source-system procedure |
| Outbound domain policy changes | Do not infer behaviour from the task’s age or saved files | Must satisfy the applicable environment and Enterprise policy layers | Run representative allow and deny tests after the policy change |
A republish notice should identify the new baseline, affected projects, reason for change, required user action and retirement date for the earlier baseline. Avoid telling users that all tasks are “updated”. The accurate instruction is that newly started tasks receive the republished setup, while owners must assess existing tasks separately.
Use the saved VM window only for short-term recovery
OpenAI’s Help Center states that saved VM state may be recoverable for up to seven days after the task was last started or resumed. The wording “up to” is important: it is a recovery qualifier, not a promise of seven full days in every case. It also concerns VM recovery, not a general guarantee covering chat retention, archival storage, source-control history or organisational backup obligations.
Do not build a work-preservation process around that window. Important code, configuration and review evidence should leave the task workspace through an approved durable system before the task becomes unavailable. Where an uncommitted workspace must be recovered, start with the documented recovery path promptly, inspect what actually returns, and then move authorised work to source control or another approved store.
Recommended recovery triage:
- Record the task identifier and the last known start or resume time.
- Attempt recovery through the currently documented product path without assuming success.
- Compare the recovered revision, working tree, generated artefacts and installed tools with the owner’s task notes.
- Rotate or revoke any credential suspected of being copied into files or logs; recovery does not neutralise secret exposure.
- Commit only reviewed, intended project files and exclude caches, build outputs and secret-bearing material.
- Open an internal incident or data-loss record if required by organisational policy.
The seven-day statement must not be used as a retention schedule. An organisation that needs defined backup, legal hold, audit preservation or disaster recovery should establish those controls in its authoritative systems rather than infer them from task recovery behaviour.
Keep repository authorisation attached to the individual account
OpenAI states that sharing an Enterprise environment does not share another person’s repository permissions or personal connections. A teammate who can use the prepared environment still needs independent authority from the source system. This remains true when the prepared filesystem contains repository-specific tools, configuration templates or convenience scripts.
Administrators should test repository access with representative accounts rather than only with the environment owner. Owner-only testing can conceal overprivileged personal connections and can also produce a false expectation that every teammate will inherit the same access. Tests should include a user with intended read access, a user with intended write access where applicable, and a user who should have no access.
| Test identity | Expected result | What the result establishes | What it does not establish |
|---|---|---|---|
| Authorised read-only repository user | Can retrieve only the repositories and references allowed by the source system | The tested account can perform the tested read operation | That other users have access, or that write operations are permitted |
| Authorised contributor | Can perform only the approved source-control operations | The tested account’s present source-system permissions | That environment sharing granted those permissions |
| User without repository access | Receives a controlled denial without repository content being exposed | The negative case for that account and operation | Universal protection against every alternative connection or cached artefact |
| User whose access has been revoked | Cannot use the revoked source-system authority | Whether revocation is effective in the tested path | That all independent credentials, exported files or prior task artefacts have been removed |
Review prepared files before sharing because they can contain repository remotes, package-registry configuration, cloud command-line profiles, certificate material or virtual private network connection details. Their presence does not grant legitimate authority, but it can disclose sensitive infrastructure information or cause a task to attempt an unintended connection. Remove personal configuration and replace it with documented placeholders or per-user setup requirements.
Separate Cloud use from workspace environment administration
OpenAI’s Enterprise admin guidance identifies distinct controls for using Codex Cloud and managing workspace environments. The exact labels, availability and role assignments can vary by plan, workspace configuration, rollout and current authorisation, so administrators must verify the live administrative surface before assigning responsibility.
As a governance pattern, permission to run Cloud tasks should not automatically imply permission to create, modify, share, republish or retire workspace environments. Environment management can alter the prepared filesystem, credential delivery, network destinations and the baseline offered to multiple users. It therefore warrants a narrower owner group, change review and an auditable publication record.
Recommended role split:
- Workspace administrator: determines who may use Codex Cloud and who may manage workspace environments, subject to organisational approval.
- Environment owner: maintains the prepared setup, documents dependencies, requests credential and destination changes, and coordinates publication.
- Credential owner: approves scope, rotation, revocation and monitoring for environment-owned credentials; this may be a different team from the environment owner.
- Repository owner: grants and revokes source-system access independently of environment sharing.
- Security or policy administrator: manages applicable Agent Security and network policy, then reviews representative allow and deny tests.
- Task user: runs authorised work, protects personal values, commits durable changes and reports mismatches between the expected and observed baseline.
This role model is a recommendation rather than a statement of universal product role names. Map it to the controls actually available in the organisation’s plan and workspace. If one person holds several roles, retain separate approval records for high-impact changes such as adding an environment-owned credential or expanding outbound access.
Apply both destination policy layers without confusing their purpose
OpenAI documents Enterprise Agent Security and per-environment internet or destination settings as separate layers. An Agent Security allowed domain does not override a more restrictive environment setting. Conversely, configuring a destination in an environment does not by itself establish that an Enterprise policy permits it.
A request should proceed only when every applicable policy layer permits the destination and the user or task has valid service authorisation. Domain allowlisting supplies neither a credential nor a legal or business basis for the operation. It also does not establish that every path, subdomain, redirected destination or operation is safe.
The documented network-secret mechanism has a narrower role. OpenAI describes proxy substitution for network secrets on allowed HTTPS destinations using port 443. That mechanism should not be generalised into a claim that all secret-bearing traffic is protected, that every protocol is supported, or that tasks cannot reveal sensitive values by other means. Direct environment variables, by contrast, are delivered to programs directly and should be treated as task-visible runtime values.
Recommended policy evaluation: for each required external operation, record the destination, port, business purpose, environment setting, Agent Security disposition, credential owner, expected account, permitted method and expected denial behaviour. Approve the smallest destination and operation set that supports the task, then test again whenever the environment or Enterprise policy changes.
| Environment setting | Agent Security setting | Expected policy outcome | Remaining requirement |
|---|---|---|---|
| Allows destination | Allows destination | Network policy may permit the tested route | Valid service authorisation, credential scope and human-approved business purpose |
| Blocks destination | Allows destination | Environment restriction remains effective | Do not weaken it merely because the Enterprise list allows the domain |
| Allows destination | Blocks destination | Enterprise policy prevents the route | Escalate through the policy-change process rather than bypassing the control |
| Blocks destination | Blocks destination | Request should be denied | Verify denial without using sensitive production credentials |
Run representative tests before and after every material change
A publication review should test the shared experience, not only the environment owner’s successful path. Use non-production accounts and synthetic, non-sensitive values where feasible. Never place protected health information, production secrets or realistic credentials in a negative test. Record the environment revision, test identity category, repository revision, applicable policies, expected result, observed result and reviewer.
Recommended minimum test suite:
- Fresh-task baseline: start a new task and verify the manifest, expected tools, project files and dependency setup.
- Workspace separation: create a task-local marker or harmless uncommitted change, then start another task and confirm the marker is absent.
- Republish boundary: publish a harmless baseline revision, verify that a new task receives it, and confirm that an existing task retains its prior files.
- Repository-positive case: test an authorised account against only the repository and operation it should access.
- Repository-negative case: test an account without access and confirm controlled denial.
- Personal-value separation: verify that a teammate is prompted to provide any required Personal vault value and does not receive the owner’s value.
- Environment-owned credential scope: perform the narrow intended operation and confirm that unrelated resources or operations are denied by the authoritative service.
- Destination-positive case: verify the approved HTTPS destination and method under both environment and Enterprise policy.
- Destination-negative case: attempt a harmless request to a deliberately disallowed test destination and confirm denial.
- Revocation case: revoke a test credential or connection and confirm that the relevant operation no longer succeeds.
- Recovery drill: document how task work is committed or exported before relying on any saved VM recovery attempt.
- Retirement case: confirm that users can identify the replacement baseline and that obsolete credentials and connections are revoked through their authoritative systems.
Passing these tests demonstrates only the observed behaviour under the recorded conditions. It is not a penetration test, a comprehensive security assessment or a compliance guarantee. Re-run affected cases after changing prepared files, credentials, source-system permissions, network destinations, Agent Security policy or workspace roles.
Exclude protected health information under the documented coverage limit
OpenAI states that Codex Cloud is not covered by its business associate agreement, so protected health information must not be processed in it; an environment name, internal approval or domain allowlist does not change that statement.
Administrators should enforce this boundary before environment publication by reviewing example data, setup files, repository fixtures, logs and external connections. Synthetic data should be checked for copied real-world identifiers, and users should receive an explicit prohibition against placing PHI in prompts, files, task workspaces, environment variables or connected services used through Codex Cloud.
If a proposed workflow may involve health information, pause the rollout and obtain review from the organisation’s privacy, security and legal owners. Do not attempt to resolve the question by interpreting this guide as legal advice or by relying on technical controls alone.
Adopt an evidence-based release decision
An environment is ready for wider sharing only when its prepared files have been reviewed, credential ownership is documented, repository tests use representative accounts, applicable destination layers produce the expected allow and deny outcomes, and the owner has explained the new-task versus existing-task boundary. A failed negative test should block publication until the cause is understood and corrected.
For republishing, classify the change before release. A routine tool update may require a new-task notice; a credential exposure, unsafe prepared file or access-policy defect may require revocation, incident handling and explicit instructions for existing tasks. Republishing alone is not remediation for credentials already exposed or files already copied into task workspaces.
Finally, retain a concise administrative record containing the environment revision, approvers, publication date, tested identities, repository scope, credential owners, permitted destinations, negative-test results, known limitations and retirement plan. This record supports later investigation without pretending that configuration evidence proves universal security or compliance.
Operational runbook for controlled environment releases
Use this runbook only after confirming that the intended owners and users can access Codex Cloud and the relevant workspace controls. OpenAI documents Cloud use and workspace environment management as distinct permissions, while actual labels, roles and availability can vary by plan, workspace setting, rollout and authorisation. Record the product surface, workspace, environment owner, approving administrator and documentation review date before changing configuration.
Required boundary: OpenAI states that its business associate agreement does not cover Codex Cloud. Do not place protected health information in the environment, repository context, task instructions, prepared filesystem, variables, secrets, logs or generated files under the cited guidance.
This procedure is a configuration and governance method, not a penetration test, security assessment or compliance guarantee. Environment publication does not replace source control, sharing does not transfer source-system permissions, an allowed domain does not confer service authorisation, and republishing does not modify tasks that already exist.
Phase A: prepare the release record
- Identify the accountable owner. Assign a named environment owner and a separate approver where organisational policy requires separation of duties. Also identify owners for each repository, credential, cloud identity, VPN connection and external destination involved.
- State the intended audience. List the workspace or authorised teammate group expected to use the environment. Do not describe the audience as “all developers” unless workspace membership, source-system access and business need have each been verified.
- Define the reusable contents. Record the tools, dependencies, configuration files and prepared filesystem elements that should become the starting point for new tasks. Exclude task-specific outputs, temporary downloads, personal notes and uncommitted work that should instead be committed or discarded.
- Create an asset register. For every variable, network secret, Personal vault requirement, prepared file and connection, document its owner, purpose, delivery path, destination, rotation authority and removal procedure. Never put an actual secret value in this register.
- Set a release identifier. Use an internal version or date that users can cite in incident reports and migration notices. This identifier is an organisational convention, not a claim that Codex provides a particular versioning feature.
- Define acceptance evidence. Specify the clean-start checks, network allow/block cases, repository access cases and secret-isolation cases that must pass before publication.
Recommended release-record template: capture the environment name, release identifier, purpose, owner, approver, intended users, repositories, prepared-file inventory, tool versions where relevant, credential classifications, destination rules, test results, publication time, superseded release and retirement conditions. Store the record in an authorised governance system rather than relying on a task conversation as the only record.
Phase B: classify every credential before configuration
OpenAI’s Cloud environment documentation distinguishes three delivery patterns. An environment variable is available directly to programs. A network secret is used through documented proxy substitution for allowed destinations over HTTPS on port 443. Personal vault values belong to an individual user; where an environment requests a specific personal value, that environment-specific value overrides a general default. These mechanisms are not interchangeable merely because each can deliver a value to a task.
| Governance question | Preferred classification | Release requirement |
|---|---|---|
| Is the value owned by the shared environment or service team and intentionally usable by authorised environment users? | Environment-owned credential, delivered only through a suitable documented mechanism | Named owner, constrained permissions, approved destinations, rotation plan and sharing review |
| Must a program read the value directly at runtime? | Environment variable may be technically relevant | Treat direct program availability as exposure; minimise scope and test that logs and files do not disclose it |
| Is the value intended for documented proxy substitution to an approved HTTPS destination? | Network secret may be relevant | Confirm destination compatibility, environment restrictions and Agent Security policy; test both permitted and denied destinations |
| Does the authority belong to each teammate rather than to the shared setup? | Personal vault | Each user supplies and governs their own value; test with separate accounts and do not seed it from the owner’s personal credential |
| Would sharing the value let teammates act as the environment owner or a privileged human? | Do not publish until authority is redesigned | Use a narrower service identity or individual authorisation, subject to organisational approval |
For OpenAI API key governance, rotation and service-account boundaries, see Govern OpenAI API Key Creation and Expiration: Service Accounts, User Keys, Maximum Lifetimes, Rotation, and Validation.
For each credential, apply a two-part test. First ask who owns the authority: the environment, a service team or an individual. Then ask how the value reaches the task: directly as a variable, through documented network-secret substitution or from the user’s Personal vault. A technically valid delivery path does not resolve an ownership mismatch. For example, putting one employee’s personal access token into an environment-owned variable would turn personal authority into shared authority without changing the underlying account’s ownership or audit semantics.
Use placeholder values during initial assembly wherever the setup can be tested without live authority. Do not embed credentials in scripts, shell history, package-manager configuration, prepared files or source-control commits. Review generated configuration and caches as well as files intentionally edited by the owner, because a prepared filesystem may contain authentication remnants or connection details that were created indirectly.
Phase C: test a clean task and the negative cases
Testing must use a new Cloud task when the purpose is to validate the reusable starting state. OpenAI states that existing tasks retain their own saved files, including uncommitted changes and installed tools. Testing only in the preparation task or another existing task can therefore produce a false pass because that task may contain state absent from the published baseline.
- Run a filesystem inventory. Check that required tools and project files exist and that temporary outputs, local histories, downloaded data and personal files do not.
- Run a source-control check. Confirm that important code and configuration are committed to the appropriate repository. Uncommitted task state is not a substitute for a durable source-control record.
- Run a clean-start dependency check. Start from the reusable setup and execute only the approved bootstrap or verification commands. Record failures rather than repairing them silently inside the test task.
- Run separate-account tests. Use authorised test users with deliberately different repository and connected-service permissions. A user without repository permission should not be expected to gain it by selecting the shared environment.
- Test Personal vault isolation. Confirm that one user’s personal value is not supplied to another user. Where the environment requests a named personal value, verify the environment-specific override and the intended behaviour when the user has not provided it.
- Test allowed network behaviour. Exercise only approved destinations and methods. Verify that the credential reaches the intended service through its documented path without appearing in ordinary output, prepared files or logs accessible to the test process.
- Test denied network behaviour. Attempt representative non-approved destinations and confirm the expected restriction. Do not infer a universal security property from one denied request.
- Test absent and invalid credentials. Ensure failure is explicit and does not fall back to a more privileged shared identity, cached session or unrelated default.
- Test least authority. Verify that the identity can perform the intended non-destructive operation but cannot perform excluded operations. Keep consequential changes subject to human-led approval and service-side controls.
OpenAI documents environment destination settings and Enterprise Agent Security as separate control layers. An Agent Security allowed domain does not override an environment restriction. Conversely, a destination permitted by both layers is not automatically authorised for a particular task: it still requires an appropriate credential, source-system permission, business purpose and human-approved operating policy.
Recommended evidence format: for each test, record the release identifier, date, tester, account type, starting state, intended result, observed result and evidence location. Redact values and sensitive payloads. A pass should mean that the defined case behaved as expected, not that the environment is secure against every attack or suitable for every workload.
Phase D: approve and publish the baseline
Before publication, compare the final prepared filesystem and configuration with the release record. OpenAI describes publishing as capturing prepared setup for new Cloud tasks. Saving configuration and publishing reusable setup are different actions, so record which action was completed and do not treat an edited but unpublished setup as available to new tasks.
- Confirm the environment contains no PHI and no data prohibited by organisational policy.
- Confirm every prepared file has a documented purpose and appropriate sharing classification.
- Confirm environment-owned credentials were approved for the intended user population.
- Confirm personal credentials remain in each user’s Personal vault rather than the owner’s shared setup.
- Confirm repositories and connected systems enforce their own permissions independently.
- Confirm required and denied destinations behaved as expected under both environment restrictions and applicable Agent Security policy.
- Confirm important changes are committed to source control.
- Confirm a clean new-task test passed from the candidate baseline.
- Record approval, publication time and release identifier.
Do not publish when the owner cannot explain a credential’s ownership, when prepared files contain unexplained tokens or sessions, when success depends on uncommitted task state, or when a clean task can act through the owner’s personal authority. Resolve the design defect rather than documenting it as an exception without appropriate security approval.
Phase E: share access without implying transferred authority
OpenAI states that Enterprise environment sharing makes the prepared setup and requirements reusable; it does not share another person’s task, personal credentials, repository permissions or personal connections. Communicate this boundary in the release notice so that users do not interpret environment visibility as permission to every referenced repository or service.
Recommended user notice: “This environment provides release [identifier] as a starting setup for new tasks. It does not grant repository or external-service access. Supply required individual values through your own Personal vault and use only services for which you are authorised. Existing tasks do not receive later environment releases automatically. Commit durable work to source control.”
Onboard at least one representative teammate before broad sharing. Ask that person to start a new task, authenticate through their own authorised accounts, verify repository access and run the acceptance checks. A test performed only by the environment owner cannot establish that personal-value separation or account-dependent source permissions work for other users.
Phase F: change and republish without rewriting task history
Treat every material change as a new release candidate. Repeat credential classification and clean-task testing when changing prepared files, installed tools, variables, network secrets, Personal vault requirements, cloud identities, VPN connections, destinations or security policy. A minor-looking dependency or script change can alter what files are created or which destinations are contacted.
- Open a change record describing the defect, requirement or risk being addressed.
- Identify whether the change affects reusable setup, individual user configuration, source-system permissions or an existing task. These require different actions.
- Build and test the candidate without using an old task as proof of the new baseline.
- Review credential ownership and prepared-file differences again.
- Republish only after the candidate passes its defined checks.
- Notify users that the new release applies to future tasks.
- Provide a human-reviewed migration procedure for work that must move from an existing task.
- Keep or retire the previous baseline according to the organisation’s release policy and current product capabilities.
OpenAI states that republishing changes the reusable setup for new tasks, while existing tasks retain their state. Do not tell users that resuming, refreshing or reopening an old task upgrades it. If a fix is required in existing work, identify the affected task, commit or export authorised durable changes, start a new task from the revised baseline where appropriate, and re-run validation. Do not copy unknown state wholesale merely to reproduce an old workspace.
OpenAI documents saved VM state as recoverable for up to seven days after the task was last started or resumed. Use that period only as a short-term recovery opportunity. It is not a promise of chat retention, backup, archive duration or recovery of another task’s uncommitted work. Urgent recovery should begin promptly, but important code and records should already be in approved durable systems.
Phase G: retire the setup and remove residual authority
Retirement must address more than environment visibility. A retired baseline may still have associated service credentials, destination rules, Personal vault requirements, prepared files, documentation and user tasks. Inventory these dependencies before disabling or removing access according to the controls currently available in the workspace.
- Announce the retirement date, replacement release and required migration actions.
- Stop new adoption through the workspace controls available to authorised administrators.
- Identify active tasks that began from the retiring setup; do not assume retiring the baseline changes those tasks.
- Require users to commit or export authorised durable work and remove prohibited local material.
- Revoke or rotate environment-owned credentials that no longer have a valid consumer.
- Remove obsolete destination allowances, network-secret mappings, cloud identities and VPN connections.
- Tell users to remove obsolete Personal vault entries where they no longer need the underlying authority.
- Update runbooks, ownership records and incident contacts.
- Retain only the release and audit evidence required by organisational policy; do not retain secret values.
- Verify that a new task cannot inadvertently select or depend on the retired setup under the current product configuration.
Release and audit checklist
Use the following checklist at publication, after material changes and during periodic review. “Not applicable” should include a reason and approver rather than being used to bypass an unresolved control.
| Control | Evidence to inspect | Failure response |
|---|---|---|
| Entitlement and role | Current workspace access, Cloud permission and environment-management authority | Pause; obtain authorised administration rather than using another person’s account |
| Named ownership | Environment, repository, credential, destination and approval owners | Do not release an orphaned asset |
| Prepared filesystem | Inventory and review of files, tools, caches and connection artefacts | Remove unexplained or sensitive material and rebuild the candidate |
| Source-control durability | Relevant commits, review references and clean status | Commit approved work or document why an item is intentionally ephemeral |
| Credential classification | Owner, delivery path, scope, destination, rotation and revocation record | Redesign any ambiguous or personally owned shared authority |
| Personal vault separation | Separate-user test with no inherited owner value | Stop sharing and investigate value delivery |
| Repository permission | Tests with accounts holding different source-system rights | Correct repository access in the source system; do not weaken environment controls as a workaround |
| Outbound access | Permitted and denied destination tests across applicable layers | Restrict destinations, correct policy and repeat tests |
| Service authorisation | Identity scope and service-side permission review | Revoke excessive authority and issue a narrower identity if approved |
| New-task baseline | Clean task created after the intended publication | Do not rely on a preparation or historical task; correct and republish |
| Existing-task notice | Release communication explaining that republishing affects future tasks | Issue a correction and provide migration steps |
| PHI exclusion | Data-classification review and user notice | Stop processing, contain exposure and invoke the organisation’s incident process |
| Retirement readiness | Replacement, credential revocation and destination-removal plan | Assign an owner and deadline before the environment becomes unsupported |
Incident response for suspected exposure or excessive authority
Follow the organisation’s approved incident process and involve security, privacy, legal or compliance personnel where required. The following is a conservative operational sequence, not a substitute for that process and not a legal determination.
- Stop further use. Pause sharing, publication and affected tasks through currently available authorised controls. Tell users not to copy, run or remove suspect files before evidence is preserved.
- Contain the authority. Revoke or rotate affected environment-owned credentials at the authoritative service. If a personal credential may be affected, have its owner and the service administrator handle revocation. Removing a value from environment configuration alone may not invalidate the underlying credential.
- Restrict destinations. Remove unnecessary destination allowances and related connections. Remember that this limits a path; it does not revoke credentials already exposed elsewhere.
- Preserve proportionate evidence. Record environment and release identifiers, affected users, task identifiers, timestamps, destinations and configuration changes. Do not place secret values into tickets or chat transcripts.
- Determine the exposure path. Check direct variables, network-secret mappings, Personal vault requests, prepared files, command output, logs, source-control history, package configuration, cloud identities and VPN connections.
- Assess task boundaries. Identify both new tasks created from the suspect release and older tasks that retained related state. Republishing a corrected baseline does not remediate those existing tasks.
- Correct and retest. Build a clean candidate, test with rotated or replacement authority, verify allowed and denied destinations, and confirm separate-user behaviour.
- Communicate precisely. State what is known, what remains under investigation, which release is affected and what users must do. Avoid claiming that allowlisting, rotation or republishing proves complete containment.
- Close with preventive actions. Update credential classification, release checks, ownership, user training and retirement procedures. Record residual risks and the accountable person accepting them.
If PHI was processed, do not assume deletion, republishing or credential rotation resolves all obligations. OpenAI’s cited Help Center guidance states that Codex Cloud is not covered by the OpenAI BAA. Escalate immediately through the organisation’s health-data, privacy and legal incident channels.
Offboarding an owner or teammate
Offboarding must distinguish personal authority from environment-owned authority. Removing a user from a workspace does not, by itself, establish that external repositories, cloud services, VPNs or saved credentials have been revoked. Likewise, rotating every shared credential is not automatically necessary when the departing person used only their own Personal vault; decide from the asset register and authoritative service logs.
When an environment owner leaves or changes role
- Assign a new authorised owner and approver before the former owner loses access where policy permits an orderly handover.
- Review prepared files, environment-owned credentials, cloud identities, connections and destination settings for personal dependencies.
- Replace credentials tied to the former owner with appropriately governed service or individual identities, subject to organisational approval.
- Rotate shared credentials when the former owner knew or could retrieve their values, or when policy requires rotation.
- Verify that runbooks, recovery contacts and release records are accessible to the successor.
- Run a new-task test under the successor’s and a representative teammate’s accounts.
When a user of the environment leaves
- Remove workspace access through the authoritative administrative process.
- Revoke repository, connected-service, cloud and VPN access in each source system.
- Require removal or revocation of relevant Personal vault values through the appropriate user or administrator process.
- Identify tasks or durable artefacts owned by the departing user and transfer only authorised business records; do not assume another user can recover uncommitted task state.
- Review whether the user had access to environment-owned credentials and rotate them according to exposure and policy.
- Record completion across all systems rather than treating workspace removal as the sole control.
Decision matrix for common operational changes
| Situation | Action | Do not assume |
|---|---|---|
| A tool or dependency must be available to future work | Prepare, test in a clean task, publish or republish, and notify users | Existing tasks receive the tool automatically |
| An existing task needs the new tool immediately | Use a reviewed task-specific migration or start a new task after preserving durable work | Republishing alters the task |
| Every user must act under their own service identity | Request an appropriate Personal vault value and preserve source-system authorisation | Sharing the environment transfers the owner’s login |
| A shared automation identity is genuinely required | Use an approved, narrowly scoped environment-owned identity with rotation and revocation controls | A broad employee credential becomes safe when renamed as an environment variable |
| A value is needed only for approved HTTPS requests using documented proxy substitution | Evaluate a network secret and constrain destinations | The secret is universally inaccessible or the destination is authorised merely because it is allowed |
| A teammate cannot access a repository | Review that teammate’s repository permission in the source system | Environment sharing grants or bypasses repository access |
| Agent Security permits a domain but the environment blocks it | Review both layers and change only through authorised policy | The Agent Security rule overrides the environment restriction |
| The environment permits a destination but Agent Security denies it | Maintain the denial unless an authorised policy review approves a change | Environment permission is sufficient |
| Uncommitted work exists in a task | Review and commit or export authorised work promptly | The published environment, another task or the recovery window is a backup |
| A task was last started or resumed several days ago | Attempt authorised recovery promptly and preserve important work durably | Recovery is guaranteed for seven days or retained afterwards |
| A credential may have appeared in a file or output | Contain, revoke or rotate at the source, preserve evidence and investigate affected tasks | Deleting the file or republishing invalidates the credential |
| The environment is no longer supported | Retire it, migrate users, revoke residual authority and remove obsolete destinations | Abandoning the setup removes existing task state or external access |
Frequently asked questions
Does publication share the task used to prepare the setup?
No. OpenAI describes publication as capturing prepared filesystem state for new Cloud tasks. A teammate receives a reusable starting setup, not the owner’s task or its conversation. Existing tasks remain separate and retain their own saved files.
Will republishing repair tasks that already exist?
No. Republishing changes the starting point for future tasks. Existing tasks retain their own state, including files, uncommitted changes and installed tools. Use an explicit migration procedure or create a new task after preserving authorised durable work.
Can environment sharing grant repository access?
No. Repository permission remains account-dependent in the source system. Test with each user class and correct missing access through the repository’s authorised administration rather than attempting to bypass it through the environment.
Is a Personal vault value safe to use without further review?
Personal vault is per-user, which supports separation from environment-owned values, but task-visible authority still requires deliberate scope, approved use and review. A user’s credential can remain excessive, expired or inappropriate even when it is stored in the correct personal location.
Does an allowed domain mean the task is authorised to call that service?
No. An allowlist controls a network path; it does not store a credential, grant a service account permission or establish business authorisation. Environment destination settings, Agent Security, credentials, service-side permissions and human-approved purpose remain separate checks.
Can Agent Security allow a domain blocked by the environment?
No. OpenAI documents these as separate layers and states that an Agent Security allowed domain does not override an environment restriction. Test the combined effective policy after either layer changes.
Are network secrets guaranteed never to be exposed?
No such universal guarantee is supported by the cited documentation. OpenAI documents proxy substitution for supported HTTPS traffic to allowed destinations. Use only that documented scope, minimise authority, test behaviour, review outputs and retain service-side protections.
Can the saved VM state replace backups or source control?
No. OpenAI documents recovery for up to seven days after the task was last started or resumed, but this is a VM-recovery qualifier rather than a backup, archive or chat-retention guarantee. Commit important work to source control and use approved records systems.
May this environment process health information if access is restricted?
No. OpenAI states that Codex Cloud is not covered by its business associate agreement, so protected health information must not be processed in it, and restricting users or destinations does not change that.
Who should approve a shared environment?
The organisation should designate authorised owners for the environment, credentials, repositories and external services, with security or administrative review according to its policies. OpenAI’s role and control documentation helps identify product permissions but does not determine an organisation’s internal approval authority.
Access 40,000+ AI Prompts for ChatGPT, Claude & Codex — Free!
Subscribe to get instant access to our complete Notion Prompt Library — the largest curated collection of prompts for ChatGPT, Claude, OpenAI Codex, and other leading AI models. Optimized for real-world workflows across coding, research, content creation, and business.
Useful Links
- OpenAI Codex documentation: Cloud environments — saving, publishing, task state, variables, network secrets, Personal vault, sharing and destination settings; accessed 30 September 2026.
- OpenAI Help Center: Using Codex Cloud — prepared environments, separate task workspaces, saved VM recovery and the boundary for the business associate agreement and protected health information; dated 30 September 2026.
- OpenAI Codex documentation: Admin rollout guide — workspace, Cloud, connected-system and environment-management controls; accessed 30 September 2026.
- OpenAI Codex documentation: Agent approvals and security — sandbox, approvals, Agent Security and environment internet-setting layers; accessed 30 September 2026.
