
ChatGPT Health Permissions and Privacy Guide: Apple Health, Medical Records, Memories, Disconnects, and Workspace Boundaries
What changed in September, and why Health permissions now need a closer look
OpenAI’s September 14, 2026 update changed the starting permission posture for new Health plugin connections: when a user connects Health after the update, ChatGPT defaults that Health connection to the user’s existing global Plugins permission setting. If the user has not changed Plugins settings, OpenAI says the default is Allow low-risk actions. This is a permission-inheritance change, not a new medical capability, not a grant of access to unconnected records, and not a waiver of consent, workspace controls, or safety confirmations.
The practical consequence is that some Health requests may use connected Health data without asking every time, depending on the user’s global plugin setting and the Health-specific setting. OpenAI’s own example draws the boundary: asking ChatGPT to email a training plan based on connected Health data to a running partner is treated as a sensitive external disclosure or action and can still require a permission step. In other words, “use my connected Health data to summarize trends” and “send my health-derived plan to another person” are not the same class of operation.
This guide treats the September update as a privacy and operations issue rather than a convenience toggle. A Health connection involves at least five separate layers: the source authorization that lets ChatGPT access a particular data source, the user’s global plugin permission posture, the Health-specific override under Settings → Plugins → Health, any workspace-level controls that apply to managed accounts, and ChatGPT’s safety or confirmation gates for sensitive actions. A less restrictive setting at one layer does not erase restrictions at another layer.
This article analyzes the 2026 ChatGPT Health launch, including medical records integration, Apple Health context, user mechanics, and the privacy landscape around OpenAI’s health feature. The complete ChatGPT Health Launches: How OpenAI’s Medical Records Integration Changes Personal Healthcare in 2026 article provides the destination-specific detail for this section’s ChatGPT Health Launch decision because it is the closest match for a launch-background marker because it directly covers ChatGPT Health’s introduction and the privacy/medical-records context the current guide discusses.
Who can use Health in ChatGPT today
OpenAI’s Health help article states that Health is rolling out gradually to eligible logged-in ChatGPT users in the United States who are at least 18 years old. The supported plans named by OpenAI are Free, Go, Plus, and Pro. Because the rollout is gradual, eligibility in the documentation does not mean every otherwise eligible user will see the feature at the same time or on every interface they use.
OpenAI lists web and iOS as supported surfaces for Health. It also states that Apple Health requires an iPhone. That dependency matters for both product planning and support: a user may be able to access ChatGPT on the web, but the Apple Health connection itself depends on Apple Health availability through an iPhone-backed environment. Voice mode and Codex do not currently support Health, so teams should not design workflows that expect health-record access in those surfaces.
Supported connection types identified by OpenAI include Apple Health, supported U.S. medical-record providers, One Medical, and Function Health. The connected experience is intended for a user’s own records. That limitation should be treated as an operating boundary: users should not connect, upload, or request analysis of another person’s records through this experience unless OpenAI’s applicable product terms and the source system’s authorization model clearly support that use.
This guide explains ChatGPT Health and how users can connect Apple Health and medical records for AI-powered wellness insights. The complete Understanding ChatGPT Health: How to Connect Apple Health and Medical Records for AI-Powered Wellness Insights article provides the destination-specific detail for this section’s Apple Health Connection decision because it directly supports the Apple Health connection section by focusing on the setup and user outcome of linking Apple Health data to ChatGPT Health.
The shortest accurate model: connected, permitted, relevant, and safe
A useful decision rule for Health in ChatGPT is: data must be connected, use must be permitted, the data must be relevant to the request, and the action must pass applicable safety or confirmation checks. Missing any one of those conditions can change the behavior. For example, a user may have connected Apple Health but disabled Health permissions; a user may allow read actions but ask ChatGPT to share health-derived information externally; or a managed workspace may restrict apps even when the individual user would otherwise allow them.
| Layer | What it controls | What it does not control |
|---|---|---|
| Source authorization | Whether ChatGPT can access a connected source such as Apple Health or a supported medical-record provider, subject to the source’s authorization flow. | It does not automatically approve every future use, disclosure, or external action involving that data. |
| Global plugin permission | The user’s general permission posture for plugins and apps, which new Health connections can inherit after the September update. | It does not grant access to data sources the user has not connected or authorized. |
| Health-specific permission | The Health override OpenAI says users can change under Settings → Plugins → Health. | It does not override safety checks, workspace restrictions, or source-level access limits. |
| Workspace controls | Administrative restrictions that may affect app availability, roles, permissions, and allowed actions in managed environments. | They do not convert Health into a clinical or covered-entity product, and they do not create a Business Associate Agreement. |
| Safety confirmation | Additional checks or prompts for sensitive actions, meaningful external effects, sensitive disclosure, or hard-to-undo operations. | It is not a guarantee that every risky request will be allowed after confirmation. |
This layered model prevents two common mistakes. The first mistake is assuming that “Allow low-risk actions” means ChatGPT can take any action involving Health data. OpenAI’s app-permission guidance describes low-risk or important-action distinctions in terms of whether an action reads data, affects something outside ChatGPT, exposes sensitive information, or is difficult to undo. The second mistake is assuming that a stricter workspace or safety decision is a bug because the user previously selected a permissive plugin setting.
What “read-only” means for Apple Health and medical records
OpenAI states that ChatGPT can read connected Health data when relevant and permitted, but it cannot update Apple Health or provider records. This read-only boundary is important for safety reviews: ChatGPT may help a user understand information from connected sources, but it is not writing new lab values, changing medication lists in a provider record, editing Apple Health entries, or placing clinical documentation into a medical-record system through the Health experience described by OpenAI.
Read-only does not mean low sensitivity. A resting heart-rate trend, lab result, medication record, sleep pattern, reproductive-health entry, or visit summary may be highly sensitive even if no external system is modified. Security and privacy reviews should therefore classify Health reads by data sensitivity and downstream use, not only by whether the operation changes a record. A summary copied into a message, email, ticket, note, or workspace chat can become a disclosure even if the original Health connection was read-only.
A practical rule for users is to separate private interpretation from external sharing. Asking ChatGPT to “summarize my last month of sleep data and list questions I may want to ask a clinician” is different from asking it to “send my sleep summary to my manager” or “email my lab trends to a training partner.” The latter class moves health-derived information outside the immediate ChatGPT conversation and should be treated as sensitive even when the underlying plugin permission is permissive.
Health can support care conversations, but it is not a diagnosis or treatment system
OpenAI describes Health in ChatGPT as designed to support, not replace, medical care. The company’s help article states that it is not intended for diagnosis or treatment. Users should treat ChatGPT outputs as informational assistance, question preparation, summarization, or organization support, not as a clinical determination. A safe use pattern is to ask for a plain-language summary of connected information and a list of topics to discuss with a qualified healthcare professional.
The distinction is especially important because Health may draw on personally relevant records, which can make the response feel more individualized than a generic health article. Personal relevance does not turn the system into a licensed clinician, a medical device, or a substitute for emergency care. Users should seek appropriate professional review for decisions about symptoms, medications, test results, diagnoses, treatment plans, or urgent conditions.
OpenAI also states that Health is not intended for clinical or covered-entity use and does not provide a Business Associate Agreement for this experience. Covered entities, clinical organizations, and healthcare vendors should not route protected health information through consumer or non-covered Health workflows merely because the data source is medical. OpenAI points covered entities to ChatGPT for Healthcare or Clinicians rather than treating the general Health feature as a HIPAA-covered workflow.
The September inheritance update does not collapse privacy boundaries
The September permission change can be summarized narrowly: new Health connections inherit the user’s global plugin permission setting, and if unchanged, the default is Allow low-risk actions. OpenAI also reported that more than 70% of Health users had already selected permission to use connected Health data without asking each time. That adoption figure should be read as product telemetry about user choices, not as evidence that all Health actions are low risk, all users should select the same posture, or every external action will proceed without confirmation.
OpenAI’s app-permission guidance makes clear that app permissions do not create new access by themselves. Available data and actions remain bounded by the connected app, the authorization granted at connection time, workspace controls, role access, action controls, parameter constraints, sync policy, and domain restrictions. In practice, a user can permit ChatGPT to use already connected Health data more smoothly, but that does not cause ChatGPT to discover records from a provider the user never connected.
Security teams should document this as an inheritance behavior, not as a blanket authorization. A precise internal note would say: “For new Health connections, the default Health permission may follow the user’s global plugin permission. Review Health-specific settings and workspace app controls before approving workflows that use health-derived information.” An imprecise note would say: “Health data is now automatically available,” which overstates both access and permitted use.
Workspace boundaries matter, especially outside personal accounts
OpenAI’s apps guidance states that availability can depend on app, plan, region, workspace, role, model, and interface. That means a user’s personal ChatGPT experience and a managed workspace experience may not match. Business, Enterprise, Edu, Healthcare, or other managed environments can introduce administrative settings, app availability decisions, role-based access, and action controls that affect whether a connection is usable or whether an action is permitted.
A workspace administrator should not assume that user-level consent is sufficient for organization-approved processing. The organization still needs a policy basis for whether users may connect health sources, whether conversations can include employee wellness data, whether external sharing is allowed, whether exports are permitted, and whether retention and deletion workflows satisfy internal obligations. Health data can be sensitive even when it originates from a voluntary consumer connection rather than an employer-sponsored record system.
For healthcare-privacy stakeholders, the critical boundary is that the Health feature described in OpenAI’s help article is not positioned as a clinical or covered-entity workflow and does not provide a Business Associate Agreement. If an organization needs HIPAA-aligned contracting, covered-workflow assurances, administrative audit controls, or clinical deployment review, it should not infer those from consumer Health availability or from plugin permission inheritance.
Memories, synced data, and chat history are separate custody questions
OpenAI states that connected medical records, Apple Health data, and conversations that use that information are not used to train foundation models or target ads. That statement is important, but it is not the only privacy question users should ask. Health data can appear in several places with different handling rules: the synced source data, the conversation text that includes or discusses that data, and memories that may be created from a conversation when memory is enabled.
OpenAI states that memories are not created directly from synced Health data. However, conversations that use Health can create memories when memory is enabled. The operational distinction is that a background sync from Apple Health should not itself become a memory, but if the user discusses health-related preferences or recurring facts in chat, memory behavior may apply. Users who want tighter separation should review memory settings before asking ChatGPT to reason across sensitive health details.
Disconnecting a Health source is also not the same as deleting every prior conversation where Health information appeared. OpenAI says disconnecting a source starts deletion of data synced from that source from OpenAI systems within 30 days, while information already included in chat history remains until those conversations are deleted. A careful cleanup plan therefore has two parts: disconnect the source to stop and remove synced-source data, and separately review or delete conversations that contain health-derived information.
How to think about the opening risk model before changing settings
Before changing Health permissions, users should classify their intended use into three buckets. The first bucket is private reading and summarization, such as asking ChatGPT to explain trends in connected data or prepare questions for a clinician. The second bucket is decision support that may influence real-world health choices, which should receive professional review and should not be treated as diagnosis or treatment. The third bucket is external disclosure or action, such as sending, posting, filing, or sharing health-derived information outside the conversation.
For the first bucket, a less interruptive permission setting may be acceptable for users who understand what sources they connected and who are comfortable with ChatGPT using relevant Health data during conversation. For the second bucket, the permission setting is not the primary safeguard; the primary safeguard is human medical judgment and avoidance of unsupported clinical reliance. For the third bucket, users should expect additional confirmation or should manually control disclosure, because the privacy risk comes from where the information goes next.
The rest of this guide walks through those layers in operational detail: eligibility checks, source connection boundaries, global versus Health-specific permissions, workspace constraints, memory behavior, retention and deletion planning, and safe review procedures for users and administrators. The central principle remains constant: a permission setting can reduce repeated prompts for low-risk uses, but it does not erase authorization, safety, medical, privacy, or workspace boundaries.
How Health permissions work when ChatGPT reads records or considers an action
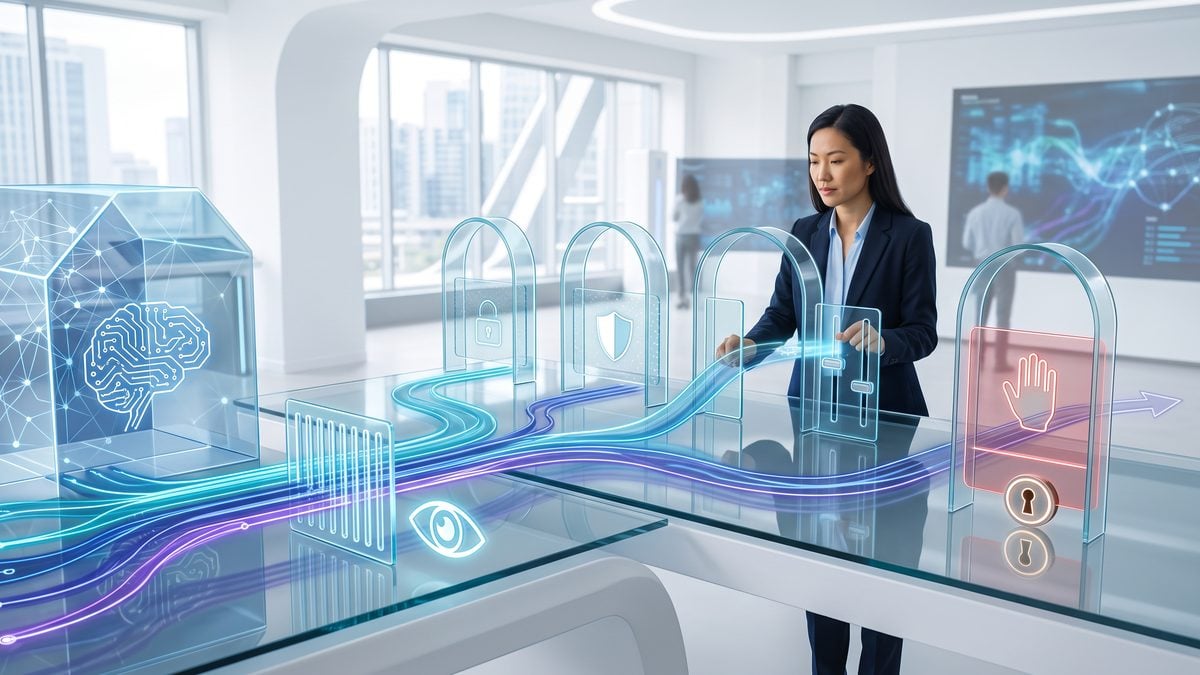
OpenAI’s September 2026 Health permission change is easiest to understand as a change to the starting posture for new Health connections, not as a change to what Health can access. For a new Health connection, ChatGPT now defaults to the user’s global plugins permission setting; if that global setting has not been changed, OpenAI says the default is Allow low-risk actions. That setting does not connect Apple Health, a medical-record provider, One Medical, or Function Health by itself, and it does not authorize data categories or accounts the user did not connect.
The permission model has two distinct layers that administrators, privacy reviewers, and advanced users should keep separate. The first layer is account authorization: the user connects a supported source and grants access through that source’s own authorization flow. The second layer is ChatGPT permission to use that already-authorized access: ChatGPT decides whether it may read or act without asking again, whether it must ask first, or whether a requested action should be blocked or confirmed because it is sensitive, external, or outside policy. Treating those layers as one control is a common governance mistake because changing a ChatGPT permission posture does not create new source access.
For Health specifically, OpenAI states that ChatGPT can read connected Health data when relevant and permitted, but cannot update Apple Health or provider records. That read-only boundary matters in practical use: asking ChatGPT to summarize recent activity metrics, compare a user-authorized lab result over time, or explain terms found in a connected record is different from asking it to write back to a medical chart, modify an Apple Health entry, or change a provider record. The latter write-back behavior is not described as supported for Health.
Permission options: what each posture should mean operationally
OpenAI’s Apps in ChatGPT documentation describes app permission options that may include Always ask, Allow read actions, Allow low-risk actions, and, for eligible apps or accounts, Allow all actions. The exact options can depend on the app, account, plan, region, workspace, role, model, and interface. For Health, the important operating principle is that a more permissive setting reduces repetitive prompts only within the data and actions already allowed by the connected source, OpenAI’s safety systems, and any workspace controls that apply.
| Permission posture | Practical meaning | Health-specific operating caution |
|---|---|---|
| Always ask | ChatGPT should ask before using the connected app or source for the relevant operation. | Useful for users who want a visible consent checkpoint each time connected Health data may be used in a conversation. |
| Allow read actions | ChatGPT may read already-authorized information without asking every time, where reading is supported and relevant. | Reading Health data can still surface sensitive facts inside the chat, so the user should confirm the account, source, and date range before relying on the output. |
| Allow low-risk actions | ChatGPT may proceed with reads and actions categorized as low risk, subject to app, authorization, workspace, and safety limits. | Low-risk does not mean “all Health uses”; external disclosure or meaningful effects outside ChatGPT can still require confirmation. |
| Allow all actions | Where available for an eligible app or account, this is a less restrictive posture for supported actions. | It does not override safety checks, workspace rules, role permissions, account authorization, parameter constraints, or blocked actions. |
Recommendation: use Always ask when a Health connection is new, when multiple people use the same device, when a user is testing which records are available, or when a conversation may involve another person’s information. Use Allow read actions or Allow low-risk actions only after the user understands which source is connected, which account is authorized, whether memory is enabled, and what kinds of follow-up requests could expose sensitive information.
This article covers ChatGPT gaining write access to connected apps such as Box, Notion, Linear, and Dropbox, and explains how those integrations expand AI workflow automation. The complete ChatGPT Gets Write Access to Box, Notion, Linear, and Dropbox: New App Integrations Expand AI Workflow Automation article provides the destination-specific detail for this section’s ChatGPT App Permissions decision because although not health-specific, it is the most relevant permissions-focused option because it deals with ChatGPT app integrations and the implications of granting access to external services.
“Always ask” is a consent checkpoint, not a substitute for reviewing the source
Always ask is the most conservative permission posture because it preserves a visible decision point before ChatGPT uses a connected app or source. In Health workflows, that checkpoint is valuable when the user wants to avoid accidental retrieval of sensitive records while asking general questions. For example, “Explain what HDL cholesterol means” can be answered generally, while “Use my connected lab results to explain my HDL trend” involves connected Health data and should be treated differently.
The checkpoint is not the same as medical review, completeness validation, or provider confirmation. A user can approve a read from a connected source and still be looking at incomplete, outdated, duplicated, or context-poor records. A safe operating pattern is to ask ChatGPT to identify the source and timeframe it used, then verify those details against the original Apple Health or provider interface before taking the output into a conversation with a clinician, caregiver, coach, insurer, employer, or family member.
Informational prompt template:
Before using any connected Health data, tell me which connected source appears relevant,
what timeframe you plan to inspect, and what limitations may exist in the available data.
Do not diagnose, recommend treatment, or assume the records are complete. Ask me before
including any information that would disclose sensitive health details to another person
or external app.
Read actions: useful for summarization, risky if the source is misunderstood
A read action is best understood as ChatGPT retrieving or using already-authorized information without changing the external source. In Health, that can support informational tasks such as summarizing categories of connected data, explaining terminology in a medical record, organizing questions a user may want to ask a clinician, or comparing values across a user-specified timeframe. None of those tasks should be framed as a diagnosis, treatment recommendation, or substitute for professional care.
The operational risk is that read access can feel passive while still revealing sensitive information. A chat summary that includes medication names, diagnoses recorded by a provider, reproductive-health information, mental-health notes, sleep patterns, location-adjacent activity signals, or lab values can be sensitive even if nothing is sent to an external service. Before using read permissions broadly, the user should decide whether the current conversation is private enough for that information and whether memory settings are appropriate for the context.
OpenAI states that memories are not created directly from synced Health data. However, conversations that use Health can create memories when memory is enabled. That distinction is important: the sync process itself is not described as writing Health facts into memory, but a conversation about those facts may still produce a memory if memory is active and the interaction fits memory behavior. Users who do not want health-related conversational facts remembered should review memory settings before starting a Health-assisted chat.
Allow low-risk actions does not authorize sensitive disclosure
The September 2026 change makes Allow low-risk actions the default for a new Health connection when the user has not changed the global plugins setting. OpenAI’s own release-note example draws the boundary: asking ChatGPT to email a training plan based on connected Health data to a running partner is a sensitive action and still requires a permission step. The reason is not that the plan is necessarily medical advice; the issue is that connected Health data would be used to disclose personal information to another person through an external action.
Example — informational, not medical: a user asks, “Look at my recent workouts and draft a plain-language summary of my weekly activity for my own notes.” That can be closer to a low-risk read-and-draft task if it stays inside ChatGPT and uses already-authorized activity data. If the user then asks, “Send that summary to my running partner,” the risk category changes because the request moves from private analysis to external disclosure. A confirmation step is appropriate even if the underlying data was already readable.
Low-risk permissions should also be interpreted alongside app-specific action controls and parameter constraints. If an app permits only certain action types, if a workspace blocks an action, or if a safety system requires confirmation, the user’s low-risk setting does not override those controls. In governance terms, Allow low-risk actions is a convenience setting within a bounded authorization envelope, not a universal release of privacy, consent, or external-sharing obligations.
Sensitive disclosure and external actions require a different review habit
Sensitive disclosure occurs when Health-derived information leaves the private context of the current conversation or is shown to someone who did not provide consent. External actions can include sending information to another person, placing information into another connected service, drafting content intended for a third party, or taking a step that may be hard to undo. OpenAI’s Apps documentation describes important-action prompts for actions that may have meaningful effects outside ChatGPT, expose sensitive information, or be difficult to undo.
Decision rule: if a request would reveal Health-derived information to a person, organization, app, workspace, or record system outside the current private chat, treat it as sensitive even if the user believes the content is harmless. This includes summaries for coaches, family members, employers, schools, insurers, teammates, and online communities. The user may choose to share, but the workflow should include an explicit confirmation step and a review of exactly what data is being included.
A safe disclosure workflow is to ask ChatGPT for a review-only draft first, with instructions not to send, post, upload, or share. The user can then remove unnecessary details, verify source accuracy, and decide whether the recipient has a legitimate reason to receive the information. For healthcare-privacy stakeholders, this mirrors a minimum-necessary habit: share only the details needed for the purpose, and do not include connected data merely because it is available.
Operational warning: permission to read connected Health data is not the same as consent from another person, permission to disclose to a third party, clinical authorization, or a Business Associate Agreement. OpenAI states that Health in ChatGPT is not intended for clinical or covered-entity use and does not provide a BAA.
App-specific overrides and workspace controls can narrow what happens
OpenAI says Health-specific permissions can be changed under Settings → Plugins → Health. This matters because a user may set a general plugin posture for convenience while wanting a stricter posture for Health. A privacy-conscious user might allow low-risk actions for non-sensitive productivity apps but keep Health on Always ask, because health data can create higher consequences when summarized, remembered through conversation, or disclosed externally.
App-specific overrides should be documented in managed environments, but the documentation should not imply that a user selection defeats workspace policy. OpenAI’s Apps guidance states that a less restrictive user selection does not override safety or workspace protections. Available data and actions remain bounded by the connected app, the authorization granted at connection time, workspace controls, role access, action controls, parameter constraints, sync policy, and domain restrictions.
Availability also varies. Apps and connected experiences can depend on the app, plan, region, workspace, role, model, and interface. OpenAI separately states that Health is rolling out gradually to eligible logged-in ChatGPT Free, Go, Plus, and Pro users in the United States who are at least 18 years old, with support on web and iOS; Apple Health requires an iPhone. Administrators should avoid writing internal guidance that assumes every user, plan, workspace, or surface has the same Health capability.
Connected-account permissions are the real data boundary
The most practical troubleshooting question is often not “Which ChatGPT permission did I choose?” but “Which source account did I connect, and what did that source authorize?” A Health connection is for the user’s own records, according to OpenAI’s Health documentation. If a user connects the wrong account, authorizes a limited source, or expects records from a provider that is not supported or not connected, ChatGPT’s output can be incomplete without being technically inconsistent with the permission setting.
Recommendation: before using Health in a consequential conversation, have the user verify the source interface directly. For Apple Health, that means confirming the relevant categories and date ranges in Apple Health on the iPhone used for the connection. For supported medical-record providers, One Medical, or Function Health, that means checking the original account or portal for the record date, ordering provider, result status, and any explanatory notes. ChatGPT can help organize questions, but the original source remains the authoritative place to confirm what was recorded.
Connected-account permissions also limit what ChatGPT can do after a user changes settings. Tightening a ChatGPT permission posture can reduce automatic use, and disconnecting a source starts deletion of data synced from that source from OpenAI systems within 30 days, according to OpenAI. However, information already included in chat history remains until those conversations are deleted. Users should not assume that disconnecting Apple Health or a medical-record source automatically removes prior chat messages that quoted or summarized Health data.
Voice and Codex are not supported Health surfaces
OpenAI states that Voice mode and Codex do not currently support Health. This is a product boundary, not a recommendation to work around the limitation by pasting sensitive records into unsupported surfaces. If a user wants Health-aware assistance, they should use a supported Health surface and connection flow rather than copying lab reports, chart notes, or Apple Health exports into a coding workspace, repository, terminal workflow, or unrelated assistant context.
Codex deserves a special caution because users may think of it as “just another ChatGPT mode.” Health is not currently supported there, and Codex workflows often involve project files, logs, command output, repositories, and technical collaboration patterns that are not designed around personal medical-record custody. Do not ask Codex to process protected or sensitive health information unless a separate, approved organizational workflow explicitly permits it and the applicable privacy, retention, and contractual requirements have been reviewed.
Voice mode also changes the privacy context because spoken interactions can be overheard, misrecognized, or initiated in a shared environment. Since Health is not currently supported in Voice, users should not expect Voice to retrieve connected Health data. If a health-related topic comes up in a spoken conversation, treat it as a general informational exchange unless the user later moves to a supported Health surface and explicitly permits use of connected records.
Pre-use checklist: source, timeframe, completeness, and consent
Before asking ChatGPT to use Health data, run a short checklist that forces the conversation to name its evidence boundary. This checklist is especially useful for caregivers helping an adult user, founders designing user education, enterprise administrators writing acceptable-use guidance, and privacy teams reviewing whether staff understand the difference between personal Health use and clinical workflows.
- Source: identify whether the request should use Apple Health, a supported U.S. medical-record provider, One Medical, Function Health, or no connected source at all. If the question is general, ask for a general explanation and avoid invoking connected data unnecessarily.
- Account: confirm that the connected account belongs to the user and reflects the user’s own records. Health in ChatGPT is intended for the user’s own records, not for silently analyzing someone else’s data.
- Timeframe: specify the date range before asking for a summary. “My recent labs” is less reviewable than “the connected lab results from March through June 2026,” because the narrower request makes missing or extra records easier to spot.
- Completeness: ask ChatGPT to state limitations in the available connected data and avoid assuming that the connected source contains all relevant medical history, medications, symptoms, provider notes, or external test results.
- Purpose: define whether the output is for personal understanding, a list of questions for a clinician, a private note, or a draft that may be shared. The purpose changes the disclosure risk even when the same data is used.
- Consent: confirm that any person whose information appears in the conversation has authorized the use. If the output will be shared with a coach, partner, employer, family member, or service, review the draft before disclosure.
- Memory: check whether memory is enabled if the conversation may include health facts the user does not want remembered through ordinary conversational memory behavior.
- Action boundary: ask for a review-only draft when unsure. Do not request sending, posting, uploading, or sharing until the user has verified the content and recipient.
Sample safe prompt: “Use only my permitted connected Health data if it is relevant. Tell me the source and timeframe you used, flag any completeness limits, and produce a private summary for my review. Do not diagnose me, recommend treatment, or send the summary anywhere. If the answer would disclose sensitive information to another person or app, ask me first.” This prompt creates an evidence boundary without asking ChatGPT to make clinical decisions or take an external action.
The strongest privacy habit is to separate three decisions that users often merge: whether ChatGPT may read connected data, whether the output is accurate enough to rely on, and whether the output should be shared. Health permissions can simplify the first decision, but they do not resolve the second or third. Users should still verify records at the source, involve qualified medical professionals for care decisions, and treat external sharing as a separate consent event.
Privacy custody after a Health connection: training, ads, memories, deletion, and exports
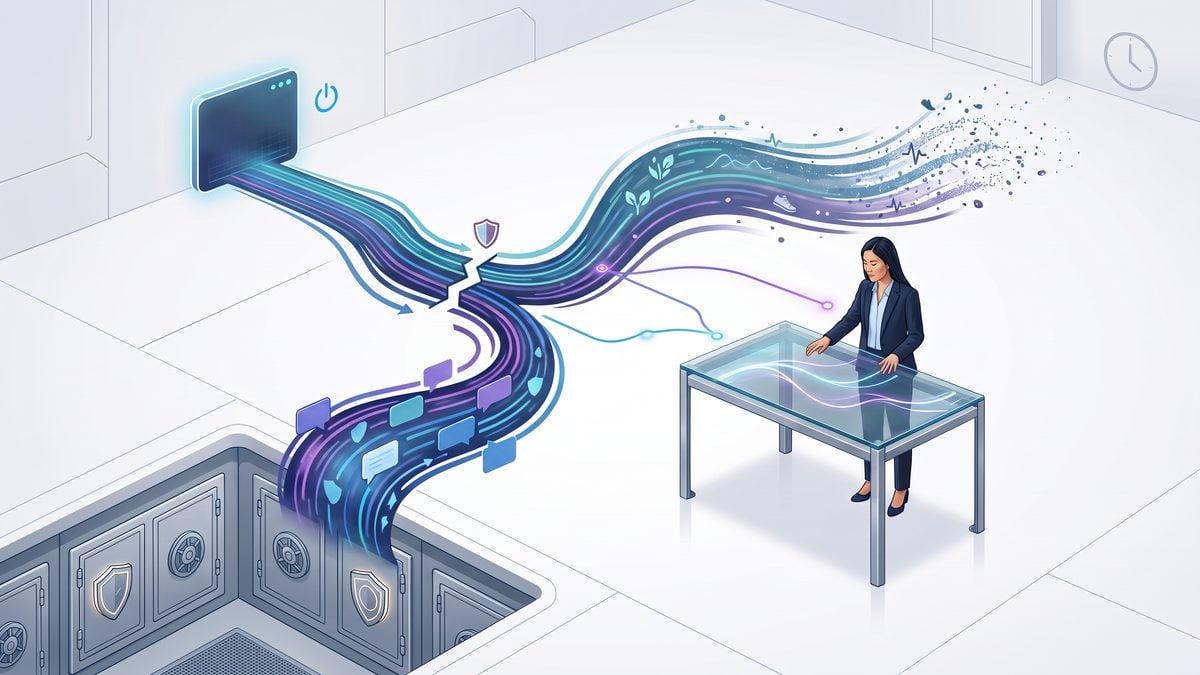
OpenAI’s Health help article draws an important custody line: connected medical records, Apple Health data, and conversations that use that information are not used to train foundation models or target ads. That statement is narrower and more operationally useful than a broad “private by default” slogan because it identifies the protected data categories and the two prohibited uses. For users and administrators, the immediate decision rule is to treat connected Health data as sensitive personal information even when OpenAI says it is excluded from foundation-model training and ad targeting, because exclusion from those uses does not remove ordinary account, chat-history, sharing, device, and deletion considerations.
The privacy model also separates synced-source data from chat content. Synced-source data is the data ChatGPT reads from a connected Health source, such as Apple Health or a supported U.S. medical-record provider, when the source has been connected and the user’s authorization allows access. Chat content is the user’s conversation with ChatGPT, including summaries, copied lab values, questions, assistant responses, and any Health-derived information that becomes part of the transcript. This distinction matters because disconnecting a Health source starts deletion of synced data from that source from OpenAI systems within 30 days, but it does not automatically erase information already included in previous conversations.
The no-training and no-ad-use statements are important, but they are not a license to overshare
OpenAI states that connected medical records, Apple Health data, and conversations that use that information are not used to train foundation models or target ads. In practical terms, a user can distinguish “model-training use” from “product operation.” ChatGPT may still need to process connected data to answer a permitted health-related request, produce a summary, compare records, or explain a term in context. The no-training statement should therefore be read as a restriction on training foundation models from that data, not as a promise that the data is never processed during the requested interaction.
The no-ad-use statement is also specific: OpenAI says this information is not used to target ads. It does not convert a health conversation into a clinical record, it does not create a HIPAA business-associate relationship, and it does not mean users should paste another person’s records into a personal ChatGPT account. The connected Health experience is intended for a user’s own records, and the safer workflow is to keep the account, device, and connected sources limited to the individual whose Apple Health or medical-record data is being reviewed.
This ChatGPT Enterprise setup guide covers admin-console configuration, SSO, data controls, and model access, providing a useful organizational contrast to the separate consumer Health retention and deletion terms described here. The complete How to Set Up ChatGPT Enterprise for Your Team: Admin Console, SSO, Data Controls, and Model Access Management article provides the destination-specific detail for this section’s ChatGPT Data Retention decision because the target explicitly addresses ChatGPT data controls and lets the bridge distinguish enterprise governance from consumer Health custody rather than conflating the two.
Memory is separate from synced Health data and separate from chat history
OpenAI’s Health documentation says memories are not created directly from synced Health data. That prevents a common misunderstanding: connecting Apple Health or a medical-record provider does not itself mean ChatGPT should create persistent memories from every metric, diagnosis code, lab value, medication list, or visit note it can read. The memory system is not described as a direct mirror of the Health sync.
The second half of the rule is just as important: conversations that use Health can create memories when memory is enabled. A user who asks, for example, “Use my connected records to help me prepare questions for my next appointment,” may produce a conversation that contains health context. If memory is enabled, the conversation itself can become a source from which a memory is created, even though the synced Health data did not directly create that memory. The operational safeguard is to review memory settings before using Health, especially if the account is used for mixed personal, family, work, or shared-device activity.
A practical pre-flight rule is to decide whether the session should be “record-aware” or “memory-light.” If the user wants ChatGPT to consult connected records but does not want ongoing personalization based on the discussion, they should review memory controls before the conversation and inspect saved memories afterward if the product surface provides that control. If the user wants long-term personalization, they should still avoid creating memories that contain identifiers, rare conditions, clinician names, insurance information, or other details that would be harmful if exposed to another person using the same account or device.
| Custody object | What OpenAI’s Health guidance says | Operational consequence |
|---|---|---|
| Synced Health data | Connected data can be read when relevant and permitted; memories are not created directly from synced Health data. | Disconnecting the source starts deletion of synced data from that source within 30 days, but users still need to manage conversations separately. |
| Conversation text | Conversations that use connected Health information are not used to train foundation models or target ads. | Health-derived details placed into chat history can remain until the conversations are deleted under applicable chat-retention behavior. |
| Memories | Health conversations can create memories when memory is enabled. | Users should review memory settings before sensitive sessions and remove unwanted memories if they appear. |
| External actions | Sensitive disclosure or meaningful actions outside ChatGPT can still require safeguards or confirmation. | Do not treat a low-risk permission posture as approval to send Health-derived information to another person or service. |
Chat history can outlive the connected source unless the user deletes the conversation
The most common deletion mistake is assuming that disconnecting Apple Health or a provider record also deletes every prior conversation that mentioned those records. OpenAI’s Health guidance says the opposite custody pattern should be expected: disconnecting a source starts deletion of synced data from that source within 30 days, while information already included in chat history remains until those conversations are deleted. A user who asked ChatGPT to summarize a lab trend, prepare appointment questions, or compare medication instructions may have Health-derived information in the transcript even after the source connection is removed.
A safe disconnect workflow has two tracks. First, disconnect the Health source when ChatGPT should no longer read updated or synced data from that source. Second, review prior conversations that used the source and delete any chats containing details the user no longer wants in chat history. This two-step approach is especially important before selling a device, leaving a shared household device, changing account access, switching workspaces, or helping a family member who accidentally used the wrong account.
OpenAI’s general chat and file retention policies should be treated as the governing reference for what happens after a user deletes chats, uses temporary-chat features where available, or deletes an account. The Health-specific 30-day synced-source deletion rule answers only one narrow question: what begins after a connected Health source is disconnected. It does not replace the broader account-level retention rules for chats, files, exports, and deletion workflows.
- Identify Health conversations before disconnecting. Search or review recent chats for conversations that summarized records, interpreted lab terminology, prepared appointment notes, discussed Apple Health trends, or copied provider data into the prompt.
- Export before deleting if the user needs a personal copy. If a conversation contains appointment questions or a plain-language summary the user wants to keep, export or otherwise preserve it according to available account controls before deleting the chat.
- Disconnect the source. Disconnecting starts deletion of synced data from that source from OpenAI systems within 30 days, according to OpenAI’s Health article.
- Delete prior conversations that should not remain. Health-derived information already included in chat history remains until those conversations are deleted.
- Review memories after the session. Because conversations using Health can create memories when memory is enabled, memory review belongs in the same cleanup checklist as chat deletion.
Export planning: keep useful records without keeping unnecessary exposure
Export is not a privacy cure; it is a custody transfer. When a user exports ChatGPT data, they may create another copy of sensitive conversations that must be protected on a local device, in email, in cloud storage, or in an enterprise records system. Before exporting Health-related chats, users should decide whether they need the full transcript, a redacted summary, or no copy at all. A full transcript may include identifiers, timestamps, provider names, conditions, lab values, and assistant responses that should not be stored casually.
A lower-risk personal workflow is to create a short, user-reviewed note before deletion rather than preserving an entire transcript. For example, a user might ask ChatGPT to produce “a concise list of questions I want to ask my clinician, without including lab values, dates of birth, addresses, insurance details, or provider portal identifiers.” The user should then inspect the output and store only what is necessary. This is a recommendation for information minimization, not a statement that ChatGPT can determine what must be retained for medical, legal, or compliance purposes.
Enterprise administrators should not instruct employees to export personal Health conversations into workplace systems unless counsel, privacy leadership, and records-management stakeholders have approved the use case. Exported files can create new discovery, retention, and access-control obligations outside ChatGPT. The safer default is to keep personal Health use in personal accounts and avoid mixing employee wellness, occupational health, benefits, or patient-related information with general-purpose workspace records.
Shared devices and shared accounts create risks that permissions cannot solve
Health permissions control what ChatGPT may do with a connected source or app connection; they do not verify that the person holding the phone or browser session is the account owner in every real-world situation. A household tablet, unlocked laptop, borrowed phone, browser profile with saved login state, or screen-shared meeting can expose Health conversations, memory content, or connected-source prompts to another person. This risk exists even when OpenAI’s no-training and no-ad-use statements apply, because the immediate exposure is local access rather than foundation-model training or ad targeting.
The simplest shared-device rule is to avoid connecting Health sources on devices or browser profiles used by multiple people. If a shared device must be used, the user should sign out after the session, close visible transcripts, avoid saving exported files locally, and verify that the connected source belongs to the same person as the ChatGPT account. Users helping a parent, partner, child, or friend should not connect that person’s records to their own account unless the product guidance, legal authority, and the individual’s consent all support the action; OpenAI describes the Health experience as intended for the user’s own records.
Screen sharing deserves special treatment because it can disclose more than the final answer. A user may reveal the connected app name, fragments of medical summaries, previous chats in the sidebar, memories, or notification content. A practical meeting rule is to use a clean browser profile, avoid opening Health-connected chats during live screen sharing, and prepare a redacted summary outside the session if the user wants to discuss a health topic with a coach, family member, or non-clinical advisor.
Clinical and covered-entity boundaries: personal Health is not a BAA-covered workflow
OpenAI’s Health article says Health in ChatGPT is designed to support, not replace, medical care and is not intended for diagnosis or treatment. It also says the experience is not intended for clinical or covered-entity use and does not provide a Business Associate Agreement. Those statements should control procurement and compliance decisions: a clinician, hospital, health plan, digital-health vendor, or business associate should not treat the consumer Health connection as a shortcut for handling protected health information in a regulated clinical workflow.
This long-form analysis examines OpenAI’s healthcare strategy, privacy and trust issues, HIPAA implications, and the point that consumer ChatGPT Health is not HIPAA-covered for general use. The complete OpenAI’s Healthcare Gambit: Privacy, Trust, and the Future of AI-Powered Personal Medicine article provides the destination-specific detail for this section’s Healthcare Privacy Boundaries decision because it is an exact semantic fit for healthcare privacy boundaries because it specifically addresses privacy, trust, HIPAA limits, and governance choices in ChatGPT Health.
Administrators should write policy language that prevents role confusion. A physician using a personal ChatGPT account to review their own Apple Health data is a different scenario from a physician pasting a patient’s chart into a non-BAA workspace. A benefits manager exploring their own wearable trends is different from an employer processing employee health information. A founder testing a wellness concept with their own records is different from running customer medical records through a general-purpose account. These distinctions should appear in onboarding, acceptable-use policies, and incident-response playbooks.
Operational warning: Do not use consumer Health connections in ChatGPT as a replacement for medical judgment, an electronic health record, a regulated clinical documentation system, or a BAA-covered processing environment. Treat the feature as a personal support surface with explicit privacy boundaries, not as a clinical compliance wrapper.
Workspace boundaries: personal Health data should not drift into managed collaboration
OpenAI’s apps and permissions guidance emphasizes that availability can depend on app, plan, region, workspace, role, model, and interface, and that a less restrictive user setting does not override safety or workspace protections. For Health data, the safer administrative posture is to prevent personal medical information from drifting into managed collaboration spaces unless a healthcare-specific agreement and policy framework expressly allow it. Workspace controls, role-based access, action controls, and approval cards are not substitutes for a BAA where one is required.
Business, Enterprise, Edu, and healthcare administrators should distinguish user-level permission inheritance from organization-level authorization. The September Health permission change for new Health plugin connections means a new Health connection may inherit the user’s global plugin permission setting, with the default described by OpenAI as Allow low-risk actions if the user has not changed plugin settings. That inheritance does not grant access to unconnected data, does not authorize all external actions, and does not override workspace restrictions, connected-source permissions, safety systems, or confirmation requirements for sensitive disclosure.
A practical workspace policy can use three tiers. Tier one permits users to discuss general health education without personal records and without diagnosis or treatment reliance. Tier two permits personal-account Health use for the user’s own records under consumer terms and personal custody practices. Tier three covers clinical, patient, employee-health, research, benefits, or covered-entity workflows and requires separate review, appropriate agreements, and healthcare-specific controls. The tiers help prevent a general “ChatGPT is allowed” decision from being misapplied to regulated health information.
| Scenario | Recommended classification | Decision rule |
|---|---|---|
| User reviews their own Apple Health trends in a personal account | Personal Health use | Use privacy cleanup steps: memory review, chat-history review, disconnect when no longer needed, and protect the device. |
| Employee pastes a patient note into a general workspace chat | Potential clinical or covered-entity processing | Do not proceed without approved healthcare workflow, agreement, and privacy review. |
| Founder tests a wellness prompt using their own exported data | Prototype with personal sensitive data | Minimize identifiers, avoid shared repositories or workspace storage, and do not use it as evidence of customer-data compliance. |
| Coach asks user to email a training plan based on connected Health data | Sensitive external disclosure | Require user review and confirmation; low-risk reading permission should not be treated as consent to disclose externally. |
A privacy-preserving session pattern for advanced users
Recommended workflow: Start each Health session by naming the source, timeframe, and purpose, and by instructing ChatGPT not to include unnecessary identifiers in the answer. A useful prompt is: “Use only my connected Health information that is relevant to preparing questions for my upcoming clinician visit. Do not include identifiers, insurance details, full dates of birth, addresses, or provider portal identifiers. Separate what my records appear to show from questions I should verify with a medical professional.” This structure keeps the output focused while reinforcing that ChatGPT is not providing diagnosis or treatment.
During the session, users should avoid asking ChatGPT to send, post, or share Health-derived information unless they are ready to review the exact content and recipient. OpenAI’s permission model distinguishes low-risk actions from sensitive external actions, and Health-related sharing can become sensitive quickly because a harmless-looking plan may reveal conditions, medications, limitations, location patterns, or provider relationships. If an approval or confirmation appears, users should treat it as a final disclosure checkpoint rather than a routine interruption.
After the session, users should run a cleanup pass: decide whether to keep the chat, delete the chat, export a minimized note, inspect memories if memory is enabled, and disconnect sources that no longer need to remain available. This procedure does not guarantee that every copy disappears immediately under every retention rule, but it aligns user behavior with the custody boundaries OpenAI describes: synced-source deletion after disconnect, chat-history persistence until conversation deletion, and separate memory behavior for Health-related conversations.
A safe operating model for Health in ChatGPT
A privacy-first Health workflow should treat ChatGPT as a read-only assistant that may help you organize, summarize, compare, and prepare questions about information you choose to connect, not as the system of record for your body, your medical chart, or your clinician’s instructions. OpenAI says Health in ChatGPT is designed to support care conversations, is not intended for diagnosis or treatment, and is not intended for clinical or covered-entity use. That operating boundary matters because the safest default is not “connect everything and ask broadly”; it is “connect the smallest useful source, ask the narrowest useful question, verify against the original record, and escalate medical uncertainty to a qualified clinician.”
The September permission inheritance change makes this operating model more important for new connections. OpenAI says new Health connections now default to the user’s global plugins permission setting; if the user has not changed Plugins settings, the default is Allow low-risk actions. That is a permission posture for how ChatGPT may use already-authorized connected access, not a new grant to Apple Health, a medical-record provider, One Medical, or Function Health. Sensitive disclosure or external actions can still require confirmation, and less restrictive user settings do not override safety, app, workspace, authorization, or approval controls.
This article compares Epic and Healthcare Public Data plugins in ChatGPT and Codex, focusing on EHR context, public evidence, permissions, and HIPAA boundaries. The complete Epic vs Healthcare Public Data in ChatGPT and Codex: EHR Context, Public Evidence, Permissions, and HIPAA Boundaries article provides the destination-specific detail for this section’s HIPAA and ChatGPT decision because it is the strongest HIPAA-specific match because it directly discusses permissions and HIPAA boundaries for healthcare data paths inside ChatGPT and Codex.
Minimum necessary connection checklist
Recommendation: before connecting any source, write down the question you are trying to answer and the minimum source needed to answer it. A medication-list review may require a medical-record source, while a sleep-trend discussion may require Apple Health data. If the question can be answered from a single lab result, appointment note, or manually pasted excerpt, connecting a broad source may create unnecessary exposure and make later cleanup harder.
- Define the purpose. Use a concrete sentence such as: “Prepare three questions for my cardiology appointment using my most recent discharge summary and current medication list.”
- Choose the narrowest source. Prefer the source that contains the authoritative record for the task; do not connect multiple providers merely because they are available.
- Confirm the account identity. Health is intended for a user’s own records, so verify that the upstream account is yours and not a family member’s, shared portal, or caregiver account.
- Review the authorization scope. Treat the upstream connection screen and ChatGPT permission posture as two separate controls: the source decides what can be connected, while ChatGPT’s permission setting affects how already-authorized access may be used.
- Use a short test question. Ask for a limited summary first, then compare the answer with the original record before asking broader questions.
Permission review: a practical decision table
| Operating situation | Safer permission posture | Required human check |
|---|---|---|
| First-time connection to a medical-record source | Start with a posture that asks before broader use, especially if you are unsure what the source contains. | Verify that ChatGPT is reading the intended person, provider, date range, and document type. |
| Routine personal trend questions, such as activity or sleep summaries | Allow low-risk actions may be reasonable only if you understand the source, the data types, and the downstream use. | Check that no sensitive disclosure, message, export, or external action is being taken without a separate review. |
| Preparing to share information with a clinician, family member, coach, or employer | Use an approval-heavy posture and review every generated summary before sharing it outside ChatGPT. | Remove unrelated diagnoses, identifiers, third-party information, and unsupported conclusions. |
| Managed workspace, employer device, or shared computer | Avoid connecting personal Health sources unless your account, device, and workspace boundaries are clearly personal. | Confirm that personal health data will not be placed into a managed collaboration context or organizational workflow. |
A useful permission review rule is to separate reading for your benefit from acting or disclosing outside ChatGPT. Reading a recent lab value to help draft appointment questions is different from emailing a training plan, sending a summary to another person, or copying a sensitive health narrative into a shared workspace. OpenAI’s apps guidance treats meaningful external effects, sensitive information exposure, and difficult-to-undo actions as higher-risk categories that may require additional approval even when low-risk actions are otherwise allowed.
Verification against original records
Every health-related output should be verified against the original source before it influences care, scheduling, medication decisions, insurance communications, workplace disclosures, or family discussions. ChatGPT can help organize connected information, but the authoritative version remains Apple Health, the medical-record provider, One Medical, Function Health, or the clinician’s direct instructions. Verification is especially important when records are incomplete, duplicated across providers, delayed after an appointment, or contain outdated medication lists.
Sample verification prompt:
Using only the connected health information relevant to my request, create a verification table with three columns: statement you are making, source record or data type it appears to come from, and what I should check in the original record before relying on it. Do not diagnose me or recommend treatment. If a fact is missing, conflicting, old, or unclear, label it as uncertain and suggest a question for my clinician.This prompt does not make the output medically authoritative; it forces traceability, uncertainty labeling, and clinician escalation points. If ChatGPT cannot identify where a statement came from, or if the source record contains conflicting dates or values, treat the result as a draft organizer rather than a usable medical summary.
Appointment preparation without turning ChatGPT into a clinician
For appointment preparation, use Health to reduce administrative friction: build a timeline, list symptoms you want to discuss, identify missing records, summarize your stated goals, and draft questions. Do not use it to decide whether to start, stop, increase, decrease, or combine medications; do not use it to interpret urgent symptoms as safe; and do not treat trend analysis as a diagnosis. A safe appointment workflow produces materials that a clinician can review, not conclusions that bypass the clinician.
- Collect context. Ask for a date-ordered timeline of relevant visits, labs, medications, and symptoms from connected records, with uncertain items flagged.
- Prepare questions. Ask for questions grouped by diagnosis, medication, test result, lifestyle concern, and follow-up logistics.
- Check omissions. Compare the summary with your portal and your own notes, then add anything missing.
- Print or copy selectively. Share only the necessary portion with the clinician; remove unrelated personal details.
- Update after the visit. Store clinician instructions in the official channel you normally use, not only in a ChatGPT conversation.
Clinician escalation rules
Use explicit escalation rules so that convenience does not become unsafe reliance. If a symptom is severe, sudden, worsening, or potentially urgent, contact emergency services or a clinician through established channels rather than asking ChatGPT to triage the situation. If ChatGPT’s answer conflicts with a clinician’s instruction, medication label, discharge paperwork, portal message, or pharmacy guidance, rely on the qualified professional or contact them for clarification.
Operational warning: Health in ChatGPT is not a diagnostic device, treatment plan, prescribing system, emergency triage line, medical-record editor, or substitute for a clinician-patient relationship. Treat outputs as drafts for discussion unless a qualified healthcare professional confirms the relevant decision.
Memory review and containment
OpenAI says memories are not created directly from synced Health data, but conversations that use Health can create memories when memory is enabled. That distinction is easy to underestimate. A synced lab value may not directly become a memory, but a conversation in which you discuss a condition, preference, goal, appointment, or limitation may still generate a memory if memory is on. Review memory settings before health-related sessions, and inspect saved memories afterward if you discussed sensitive facts you do not want reused later.
A practical memory rule is to avoid turning transient health context into durable personalization unless there is a clear benefit. For example, “I prefer appointment summaries in bullet points” may be a useful general preference; “I have a specific diagnosis and take a specific medication” may be more sensitive than necessary for future chats. If you use memory, keep only durable preferences that improve usability without preserving unnecessary medical detail.
Periodic disconnect review
Set a calendar reminder to review Health connections and permissions after major appointments, provider changes, new diagnoses, device changes, or account-sharing changes. A connection that was appropriate for preparing one specialist visit may no longer be necessary two months later. OpenAI says disconnecting a source starts deletion of synced data from that source from OpenAI systems within 30 days, but information already included in chat history remains until those conversations are deleted.
Recommended review cadence: review active Health sources monthly while you are actively using them, immediately after a one-time purpose is complete, and whenever you change devices or share access with another person. During each review, record which sources remain connected, why each is still needed, which permission posture applies, whether any sensitive chats should be deleted, and whether memories should be removed or edited.
Incident response for over-connection, wrong-account access, or accidental disclosure
Create a small incident playbook before something goes wrong. Common privacy incidents include connecting the wrong upstream account, discovering that a shared device exposed a conversation, pasting a ChatGPT health summary into a work channel, or realizing that a conversation retained information after a source was disconnected. The first response should be containment: stop the session, avoid further sharing, disconnect the mistaken source if appropriate, and preserve enough local notes to understand what happened without unnecessarily copying more health data.
- Contain. End the active conversation if it is pulling the wrong records or producing content for the wrong audience.
- Disconnect or narrow. Remove the source or change permissions if continued access is not necessary.
- Review chat history. Identify conversations that include synced Health information and delete those that are no longer needed.
- Review memories. Remove any memory that captured sensitive health context from the conversation.
- Notify the right party. If the incident occurred in a workplace, clinical, school, or regulated context, follow the applicable privacy, security, legal, or compliance reporting process rather than handling it informally.
- Document corrective action. Record the date, source, permission change, deleted conversations, memory review, and any downstream recipients who received the information.
Deletion evidence and recordkeeping
Deletion evidence should be simple, dated, and proportionate. For a personal user, a private note may be enough: source disconnected, approximate time, related conversations deleted, memories reviewed, and downstream copies removed where possible. For an organization investigating accidental use of personal Health data in a managed context, evidence should follow internal retention, legal, and privacy procedures; do not create extra copies of health content just to prove that it existed.
Do not assume that disconnecting a Health source erases everything that appeared in a chat. OpenAI’s Health guidance separates deletion of synced-source data after disconnect from information already included in chat history. The operational consequence is straightforward: if the goal is to remove health content from ChatGPT history, review and delete the relevant conversations as a separate step, and then check memory settings as a third step.
What Health does not do
- Health does not update Apple Health or provider medical records; OpenAI describes the connected Health experience as read-only.
- Health does not replace medical care, diagnose conditions, prescribe treatment, or provide emergency triage.
- Health does not make Voice mode or Codex Health-aware; OpenAI says Voice mode and Codex do not currently support Health.
- Health does not provide a Business Associate Agreement for clinical or covered-entity workflows.
- Health does not authorize access to data you did not connect through the relevant source and account authorization process.
- Health does not make low-risk permission settings equivalent to permission for sensitive disclosure or meaningful external action.
- Health does not automatically delete prior chat history when you disconnect a source.
- Health does not directly create memories from synced Health data, although conversations using Health can create memories when memory is enabled.
- Health does not eliminate the need to verify outputs against original Apple Health, provider, One Medical, or Function Health records.
Conclusion: keep the assistant useful by keeping the boundary visible
The safest way to use Health in ChatGPT is to make every session purpose-bound, source-aware, and reviewable. Connect only what the task requires, use permission settings that match the sensitivity of the data, verify generated summaries against original records, and escalate medical uncertainty to qualified clinicians. Treat memory, chat history, synced-source data, and downstream sharing as separate custody questions, because each has a different privacy consequence.
The September permission inheritance change reduces friction for some new Health connections, but it does not remove the user’s responsibility to understand what is connected, what is being read, what might be shared, and what remains after disconnect. A good Health workflow is not measured by how much data ChatGPT can see; it is measured by whether the user can explain why each source is connected, what question it supports, how outputs were verified, and how unnecessary data will be removed when the purpose is complete.
Access 40,000+ AI Prompts for ChatGPT, Claude & Codex — Free!
Get instant access to our complete Notion Prompt Library — the largest curated collection of prompts for ChatGPT, Claude, OpenAI Codex, and other leading AI models. Optimized for real-world workflows across coding, research, content creation, and business.
Useful Links
- OpenAI Help: Health in ChatGPT
- OpenAI Help: Apps in ChatGPT
- OpenAI Help: Chat and file retention policies in ChatGPT
- OpenAI Help: ChatGPT release notes
